Discovery and inventory
Find the certificates you didn't know about.
Scan your network, pull inventory from other CAs, and watch Certificate Transparency logs for certificates issued in your name. Risky endpoints are flagged and can be accepted as risk with approval.
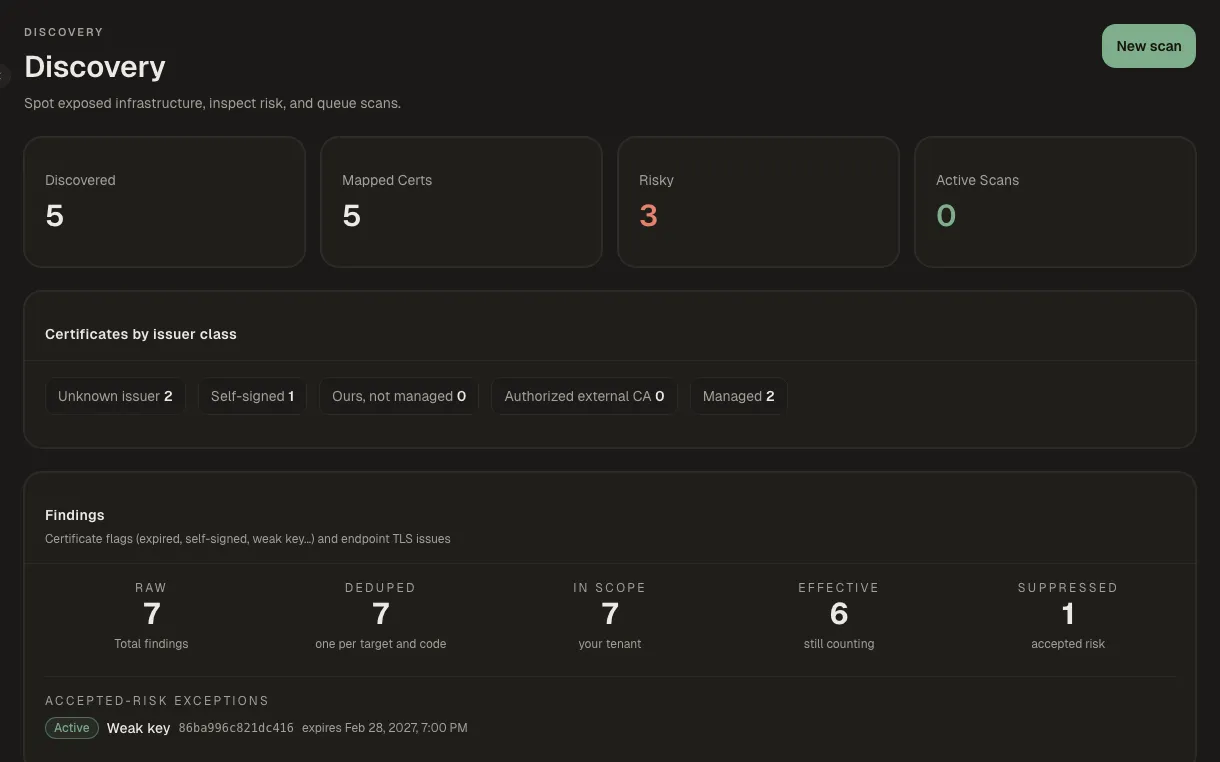
How it works
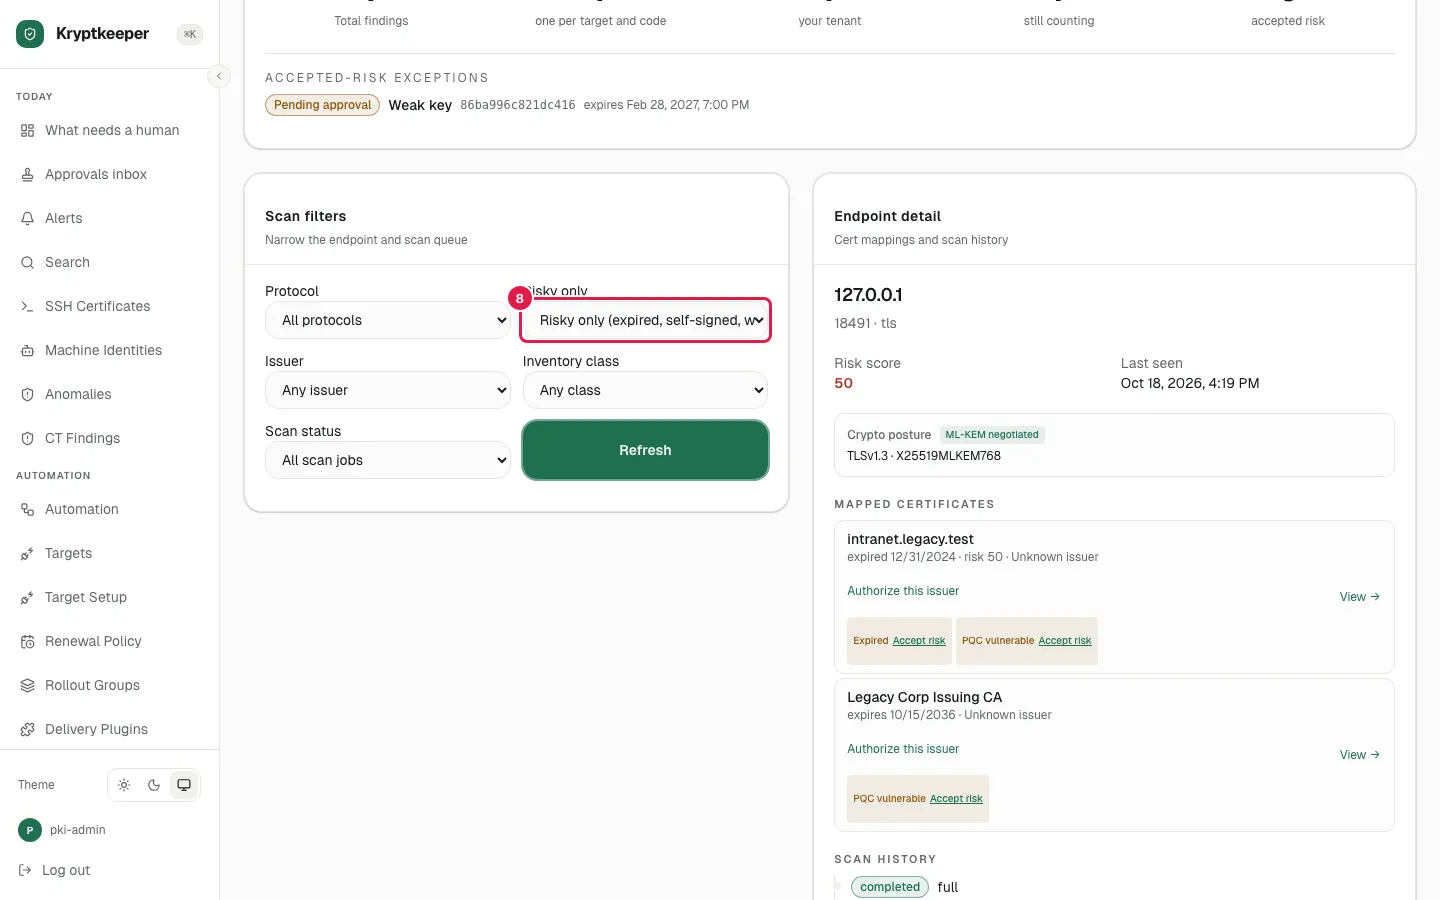
Run a discovery scan
Scan a range and read what was found.
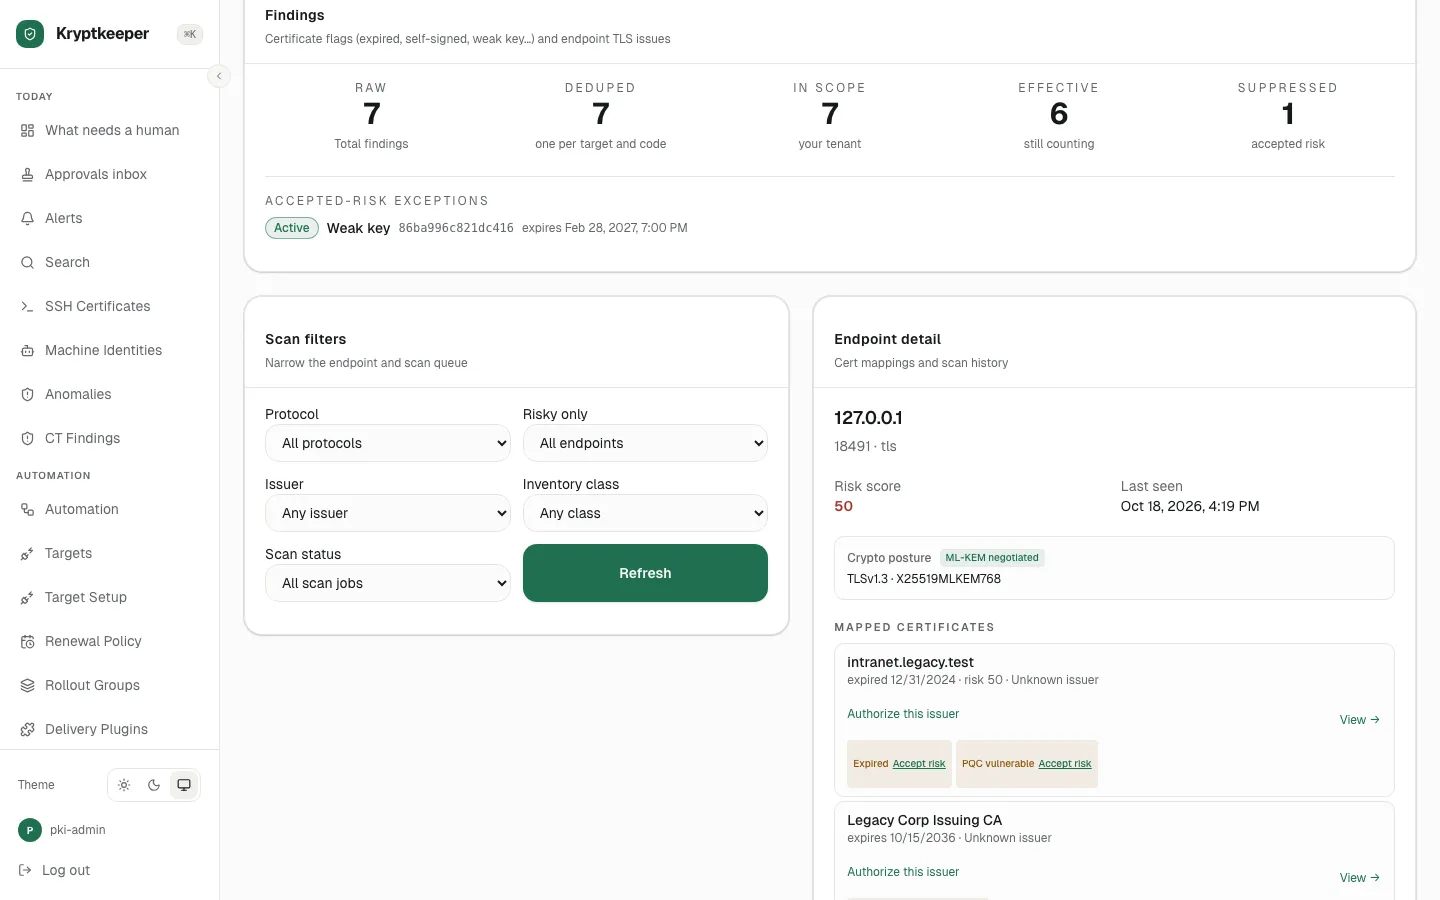
Inspect an endpoint and accept a risk
Open a risky endpoint and propose a risk exception for approval.
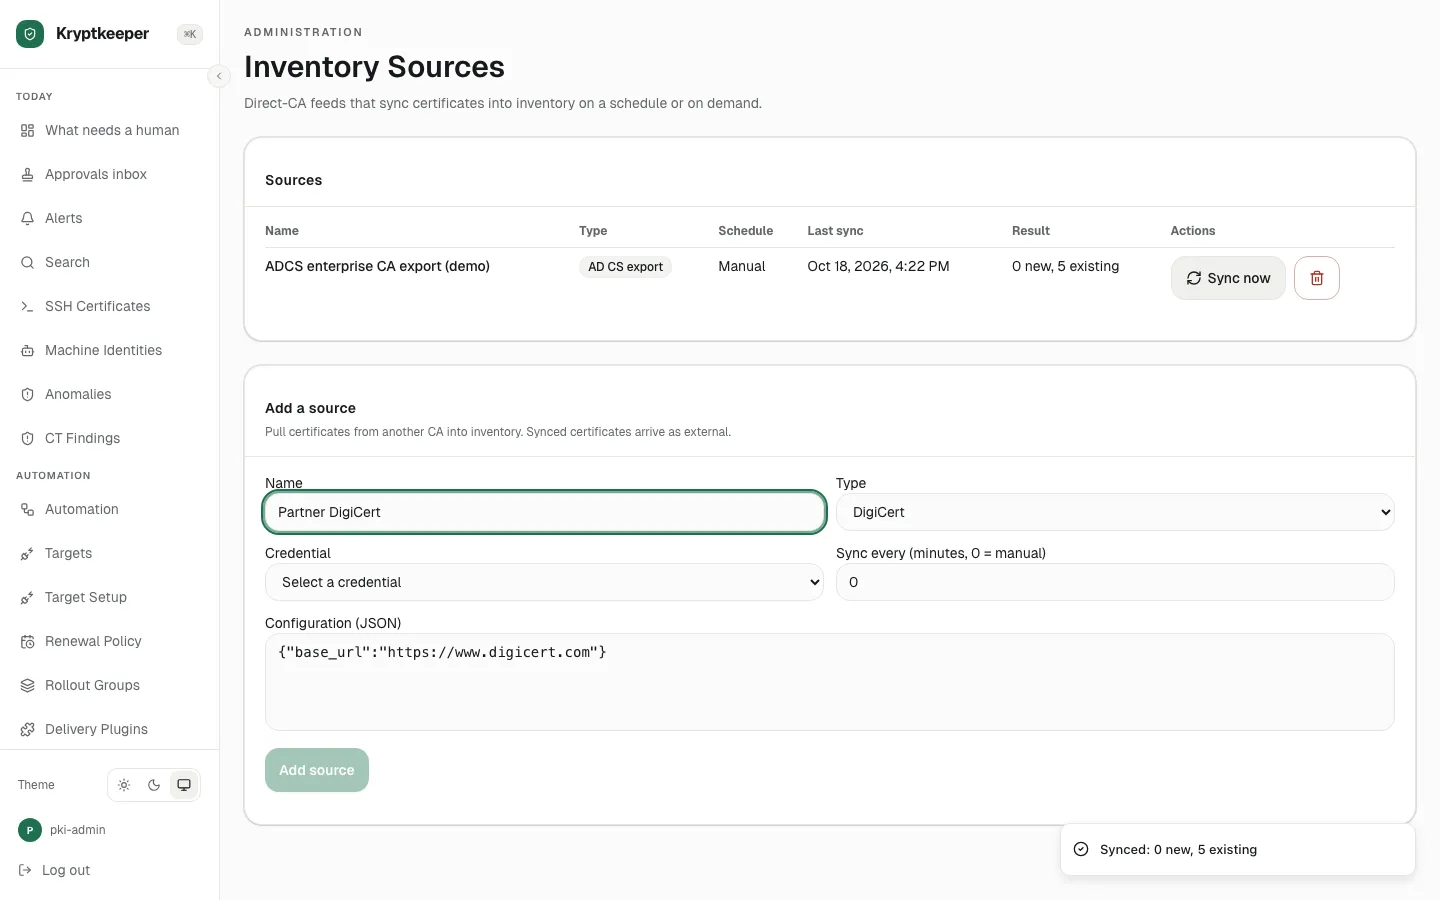
Sync certificates from another CA
Pull the inventory of another CA into one view.
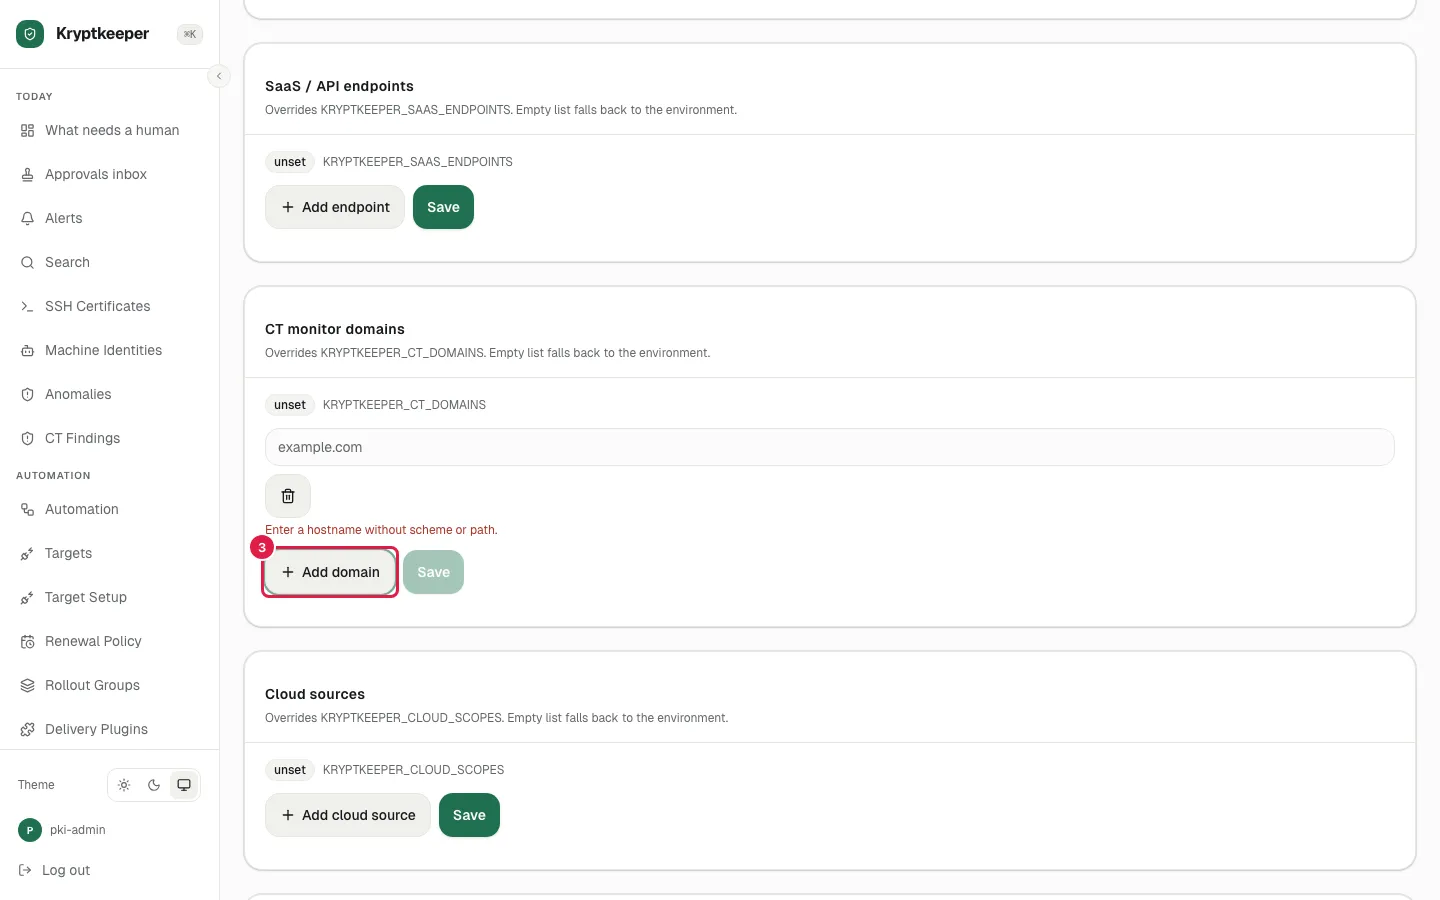
Monitor Certificate Transparency
See certificates issued for your domains by anyone.
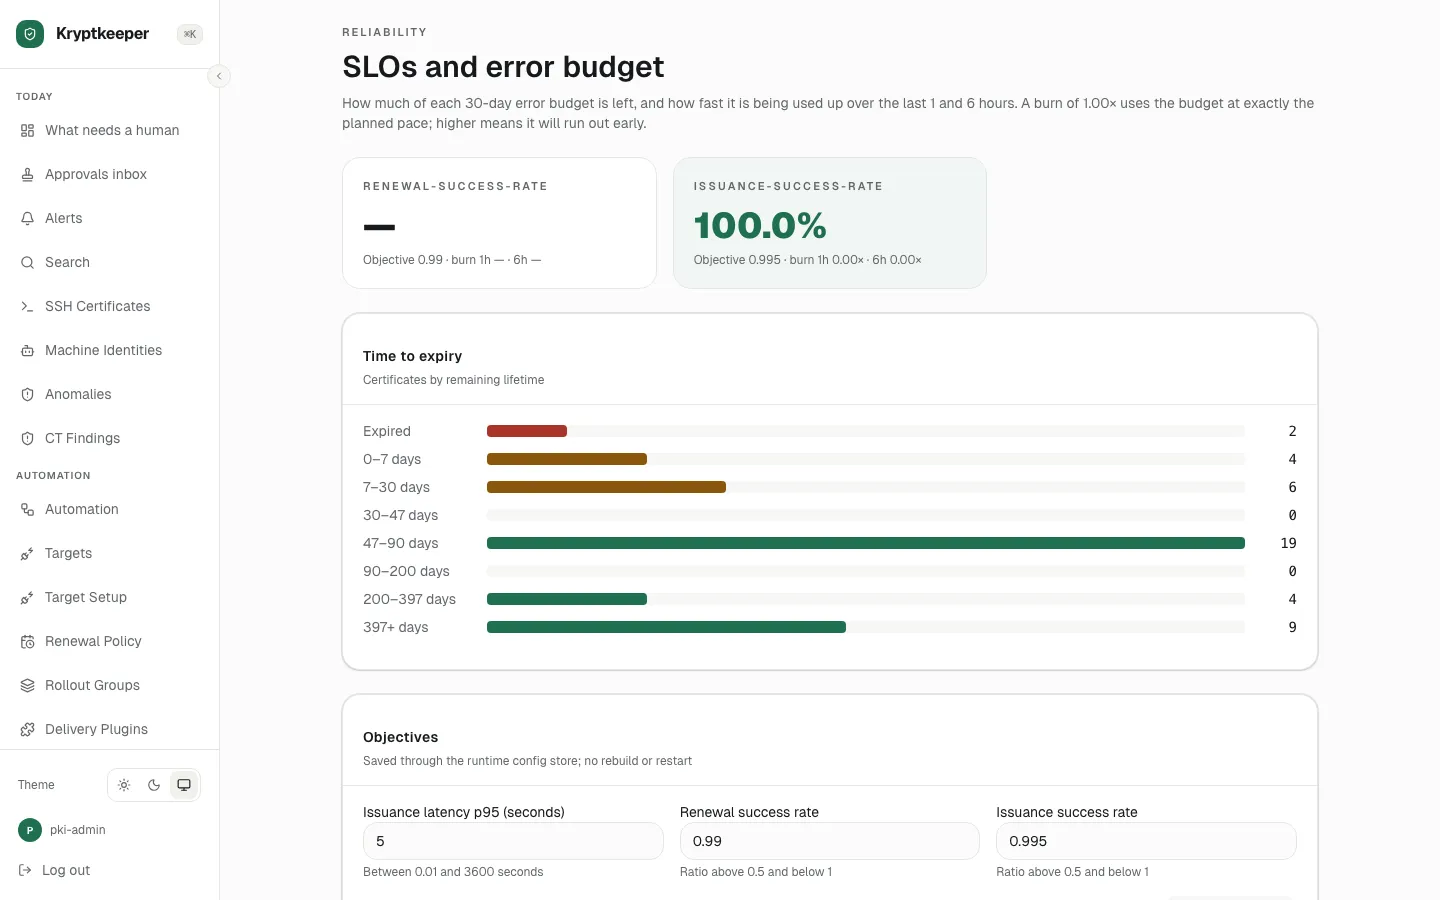
Review issuance anomalies
Spot unusual issuance once the scheduled scan has run.
Docs
Paths that use this
- Take over an existing estate for Security lead