Machine and workload identity
Identities for workloads, SSH and code signing in the same place.
Approve machine identities before they exist, issue SPIFFE SVIDs to workloads, sign SSH certificates, and keep code-signing certificates in their own inventory.
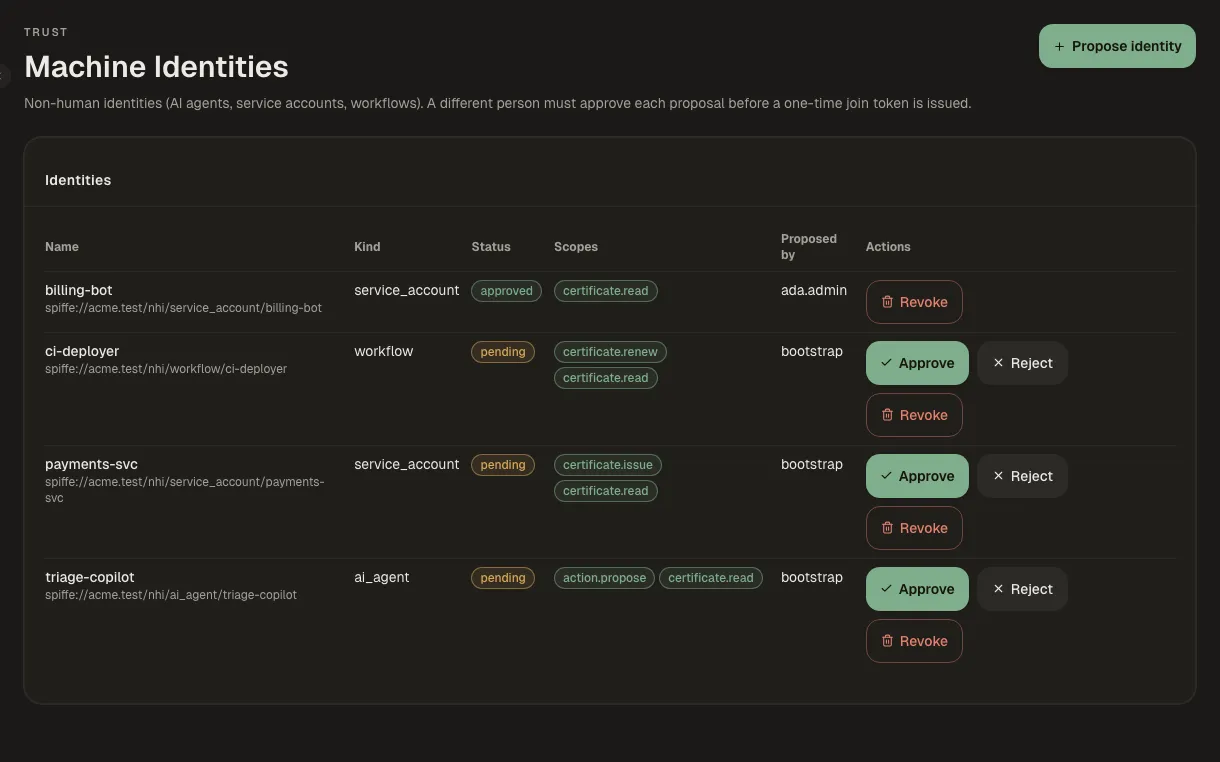
How it works
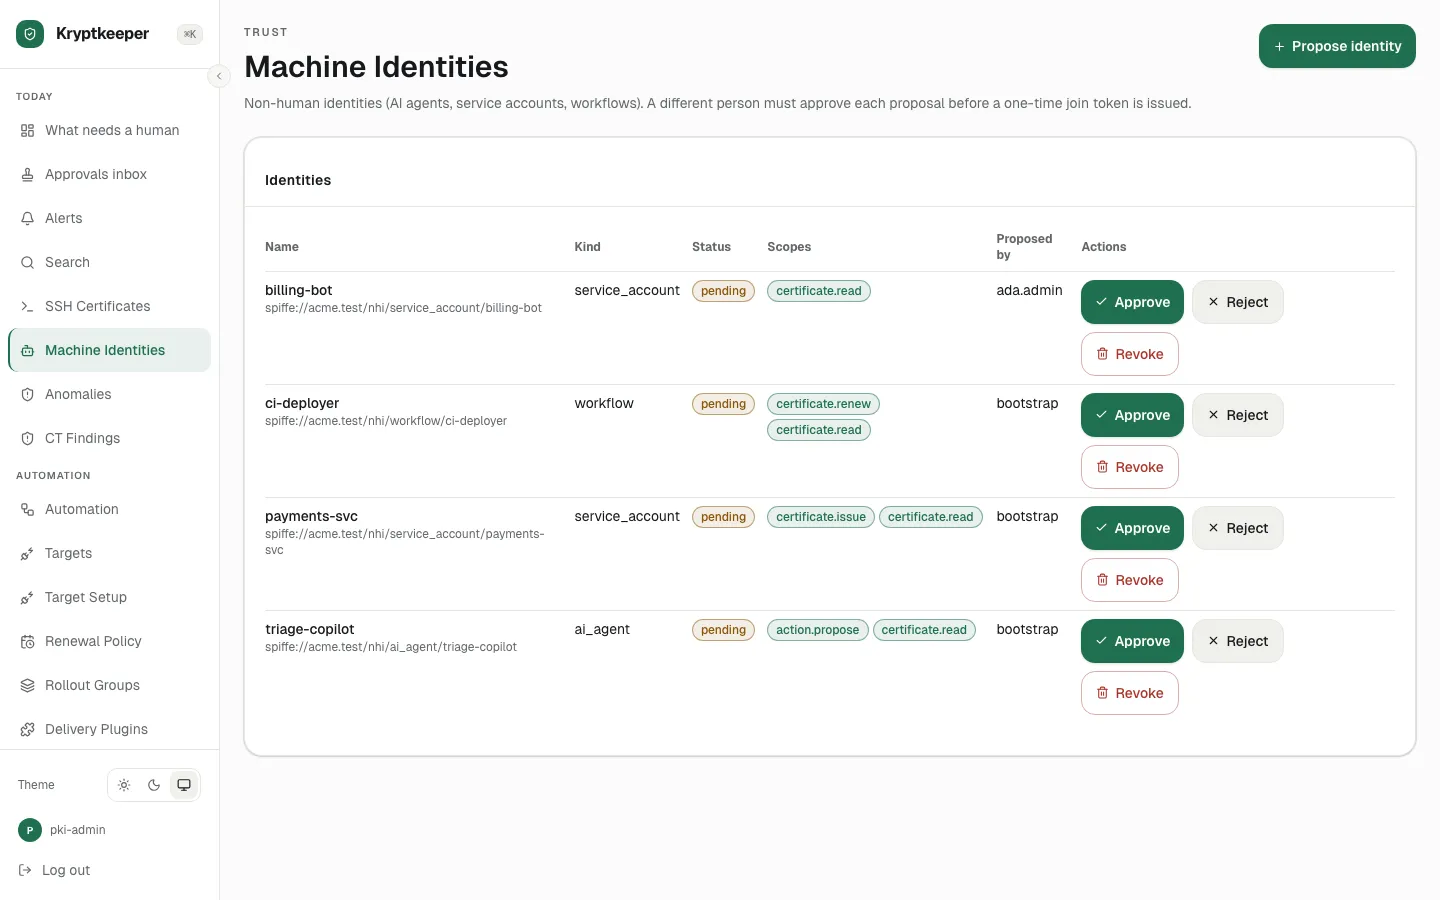
Propose and approve a machine identity
One person proposes a machine identity and another approves it.
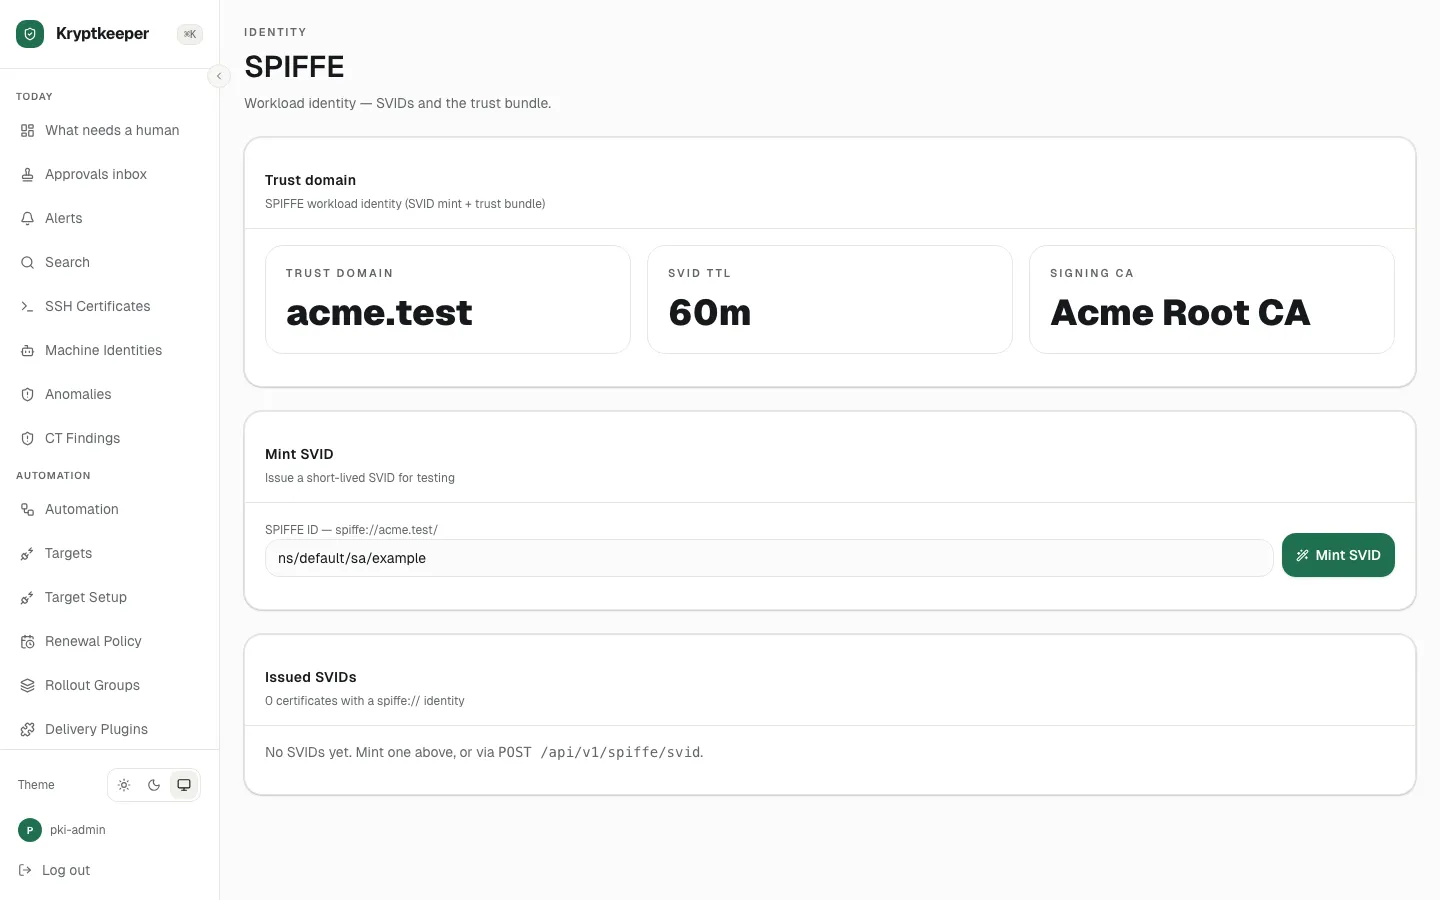
Issue SPIFFE SVIDs
Issue workload identities from a signing CA.
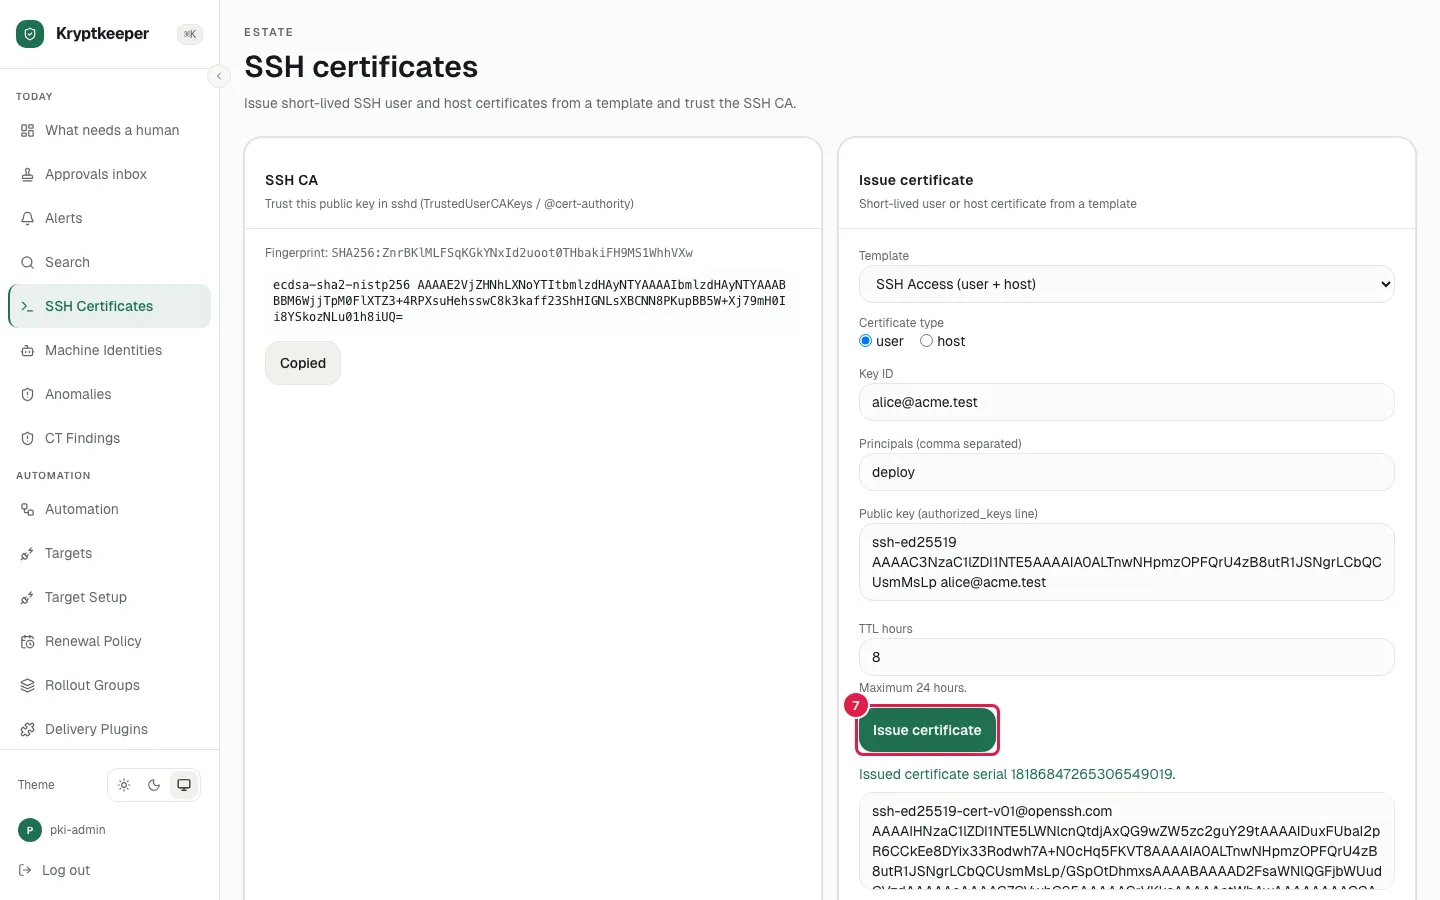
Issue SSH certificates
Sign SSH user and host certificates.
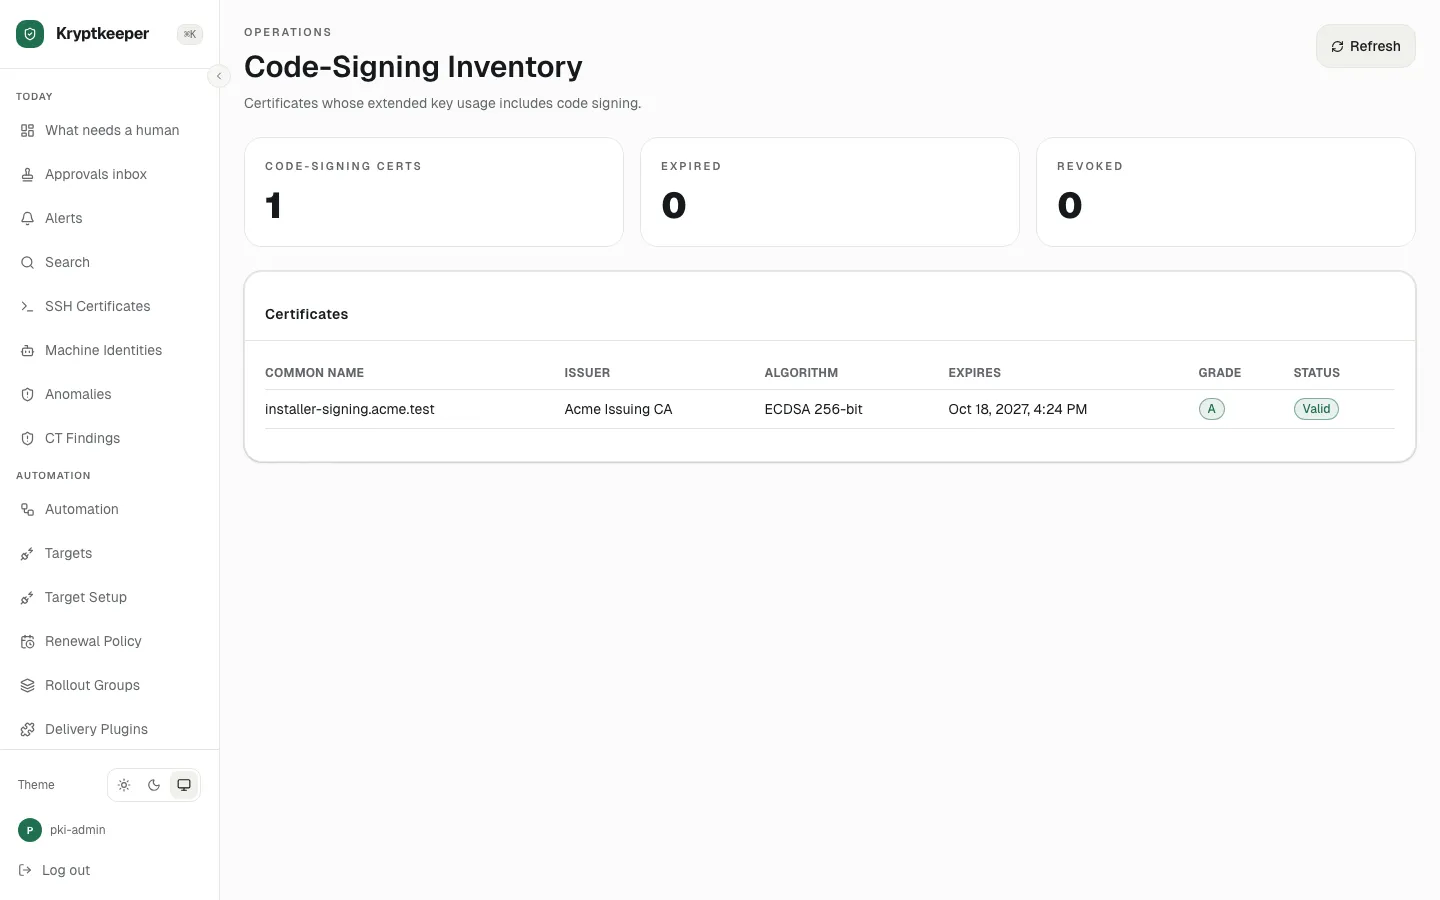
Use the code-signing inventory
Track code-signing certificates and who may use them.
Docs
Paths that use this
- Machine and workload identity for Platform engineer