What's new in 1.2
ACME clients that only send a CN now fit a CA with name constraints.
Version 1.2 lets a template fix subject components such as DC, O, OU, L, ST and C, appended after the CN of every certificate issued under it. ACME clients can only send a CN, so this is how they fit an issuing CA with directoryName name constraints. The CA also refuses, before it signs, any certificate its issuing CA's name constraints would make invalid. Version 1.2.1 is a patch release. These walkthroughs show each screen that exists in the console today.

How it works
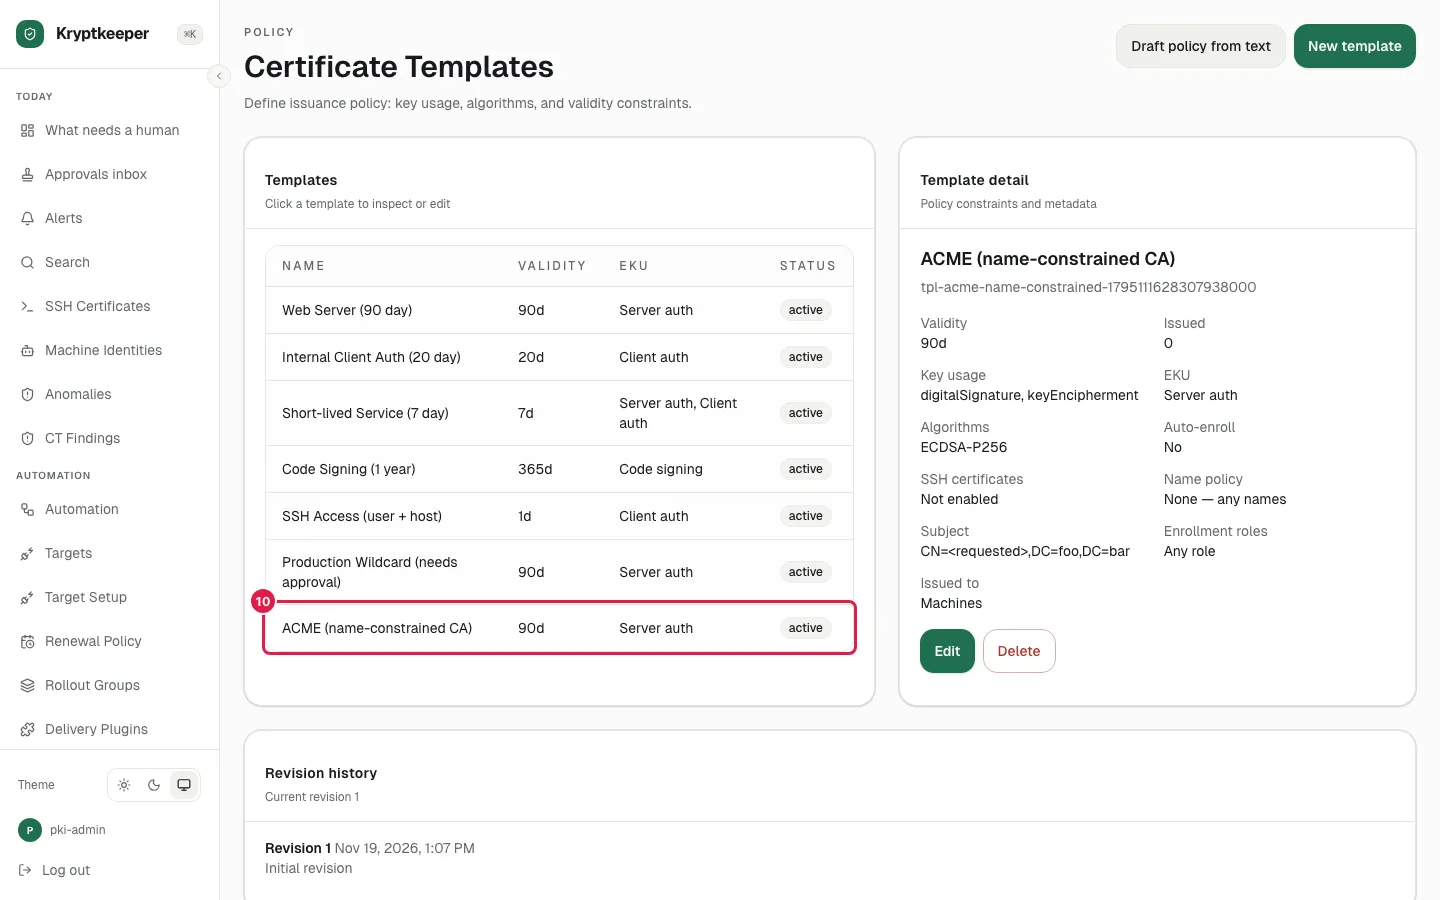
Fit ACME clients to a name-constrained CA
Create a template that fixes DC=foo,DC=bar after the CN, then read it back on the template detail.