Govern it and prove it
Least privilege, a second person on sensitive changes, and evidence an auditor will accept.
7 walkthroughs, in order
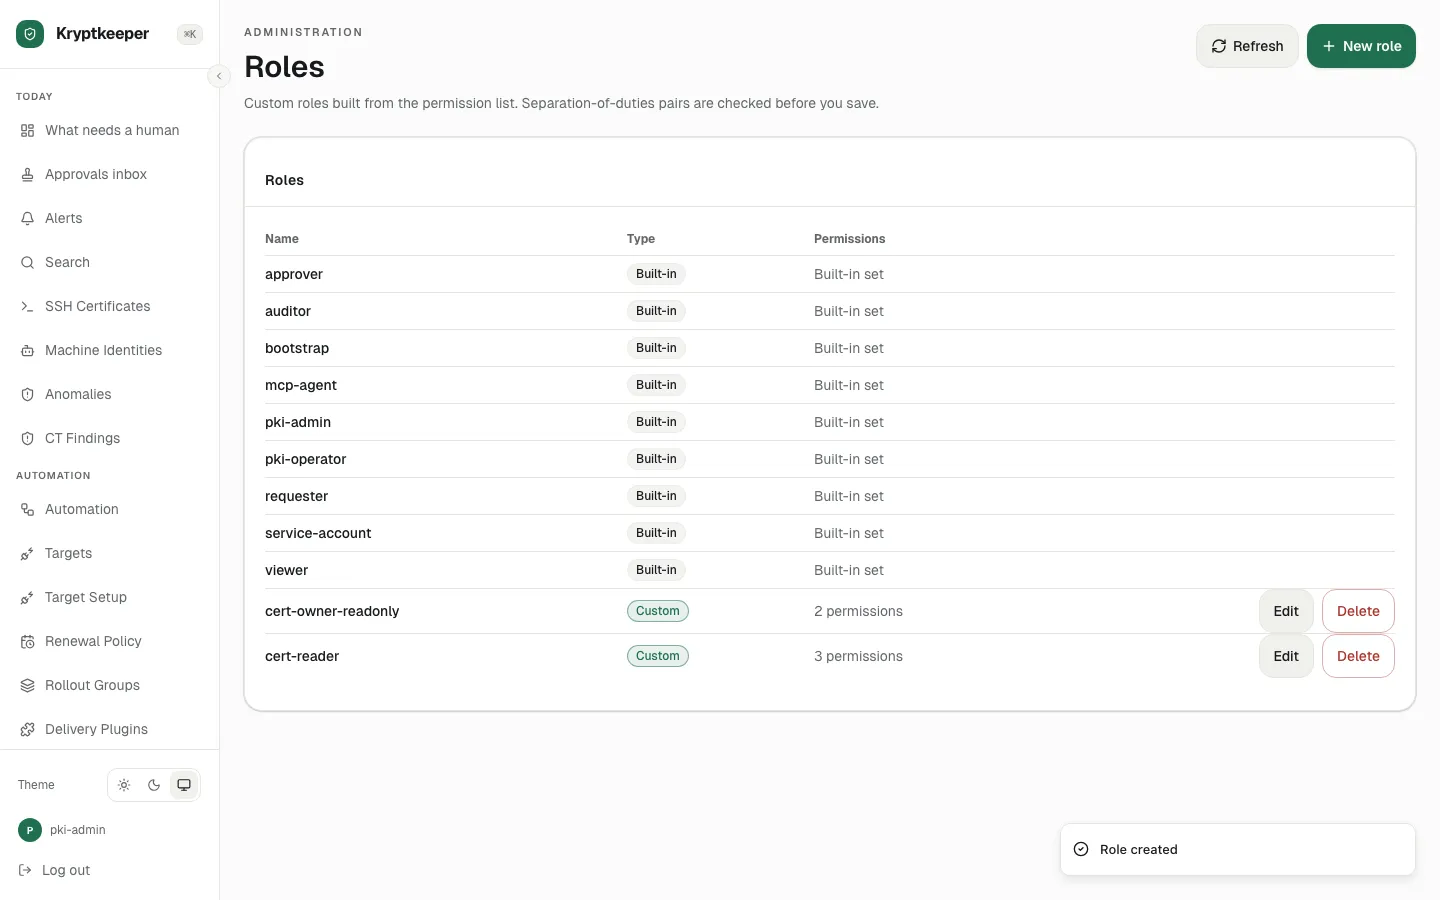
Access and tenancy Create a least-privilege role
Build a role with only the permissions a job needs.
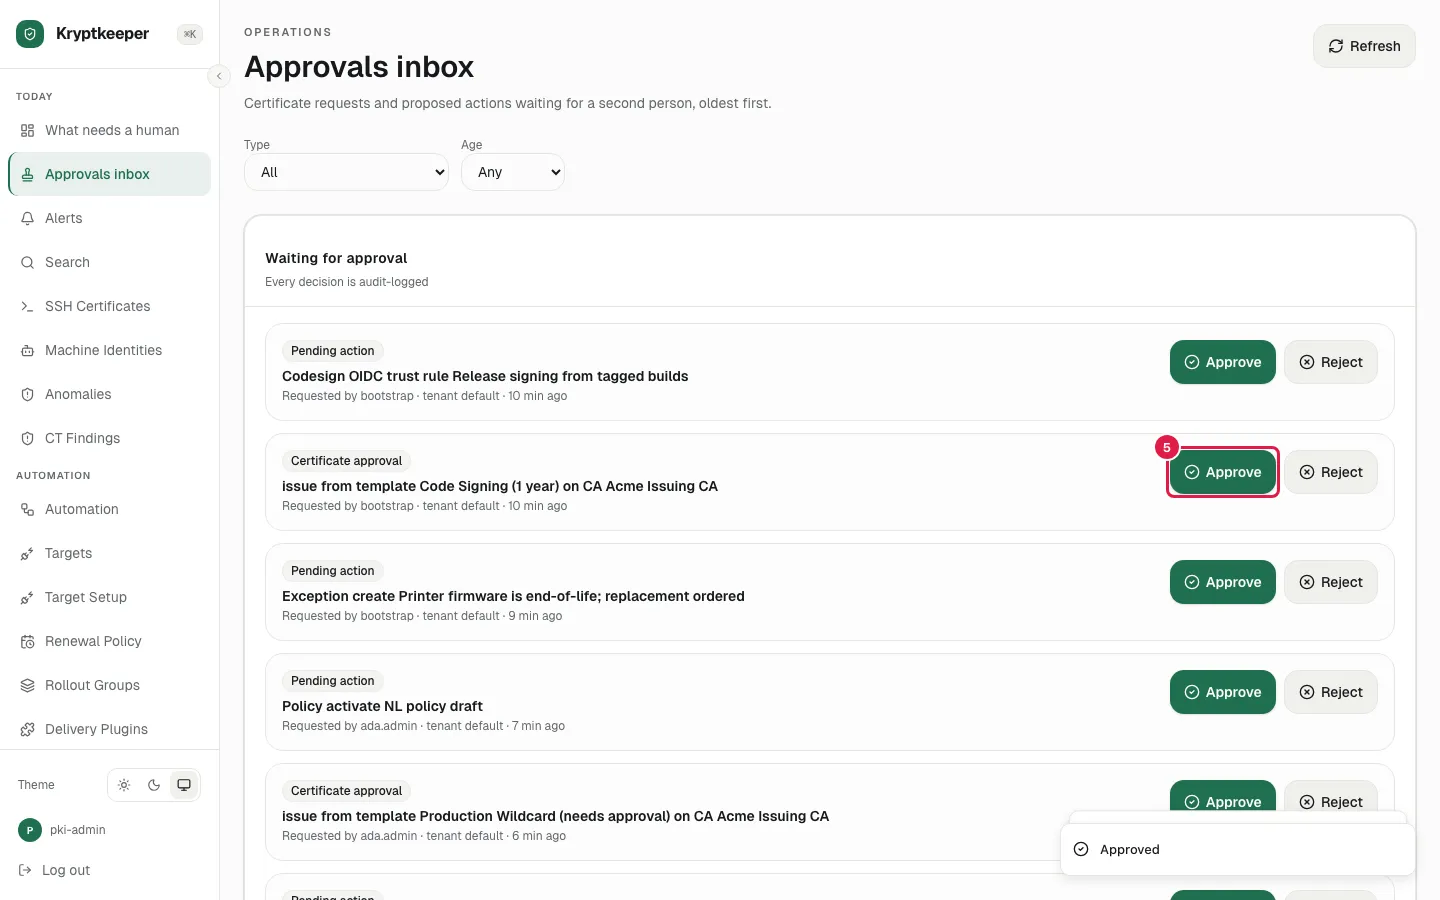
Approvals and guardrails Approve a pending request
A second person reviews and approves a certificate request.
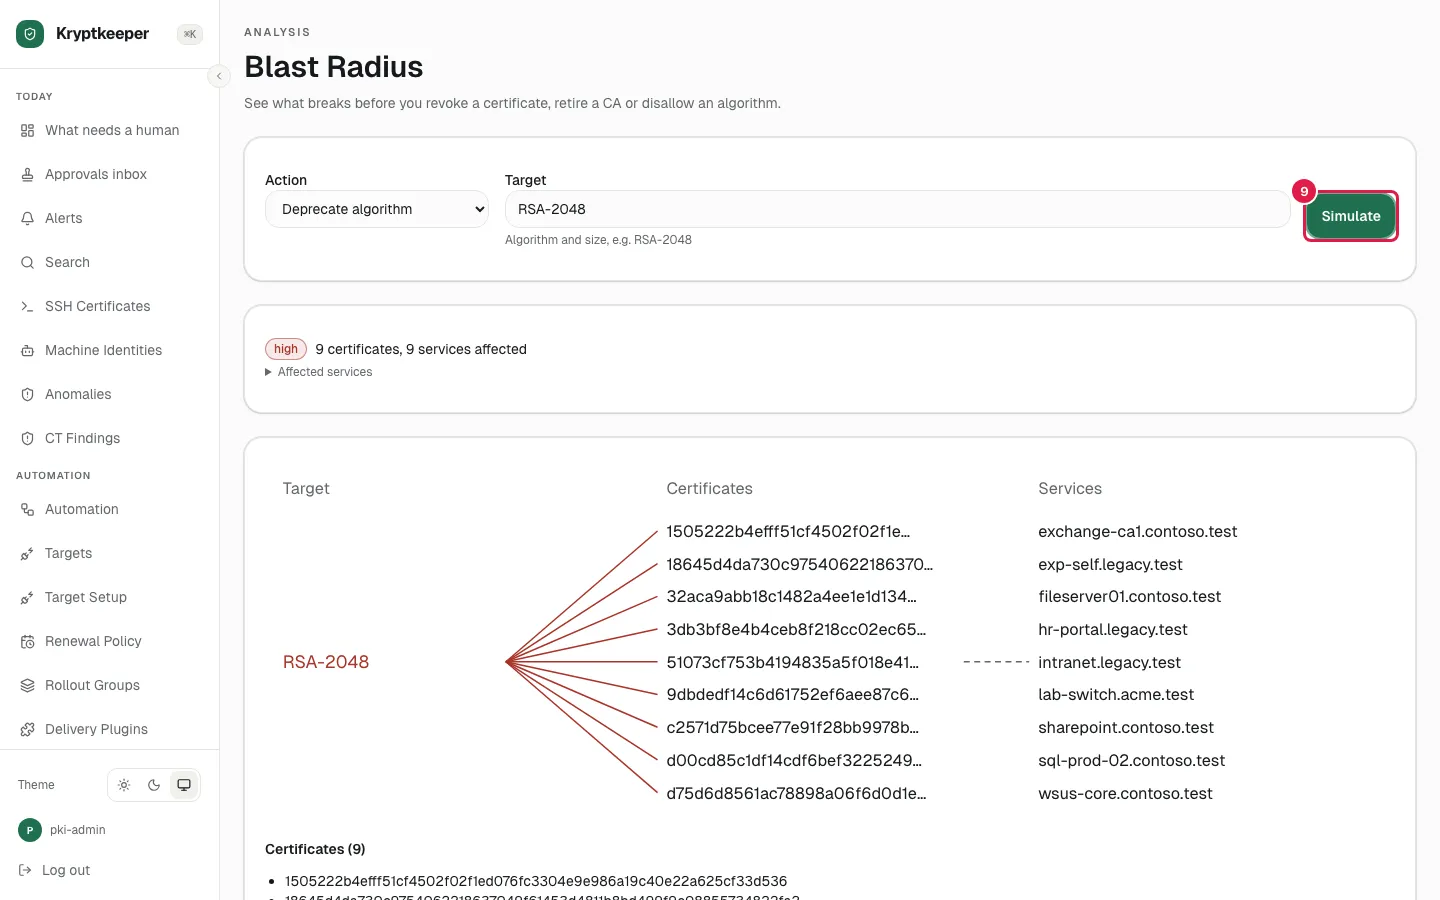
Approvals and guardrails Check the blast radius first
See every certificate and service a destructive change would affect.
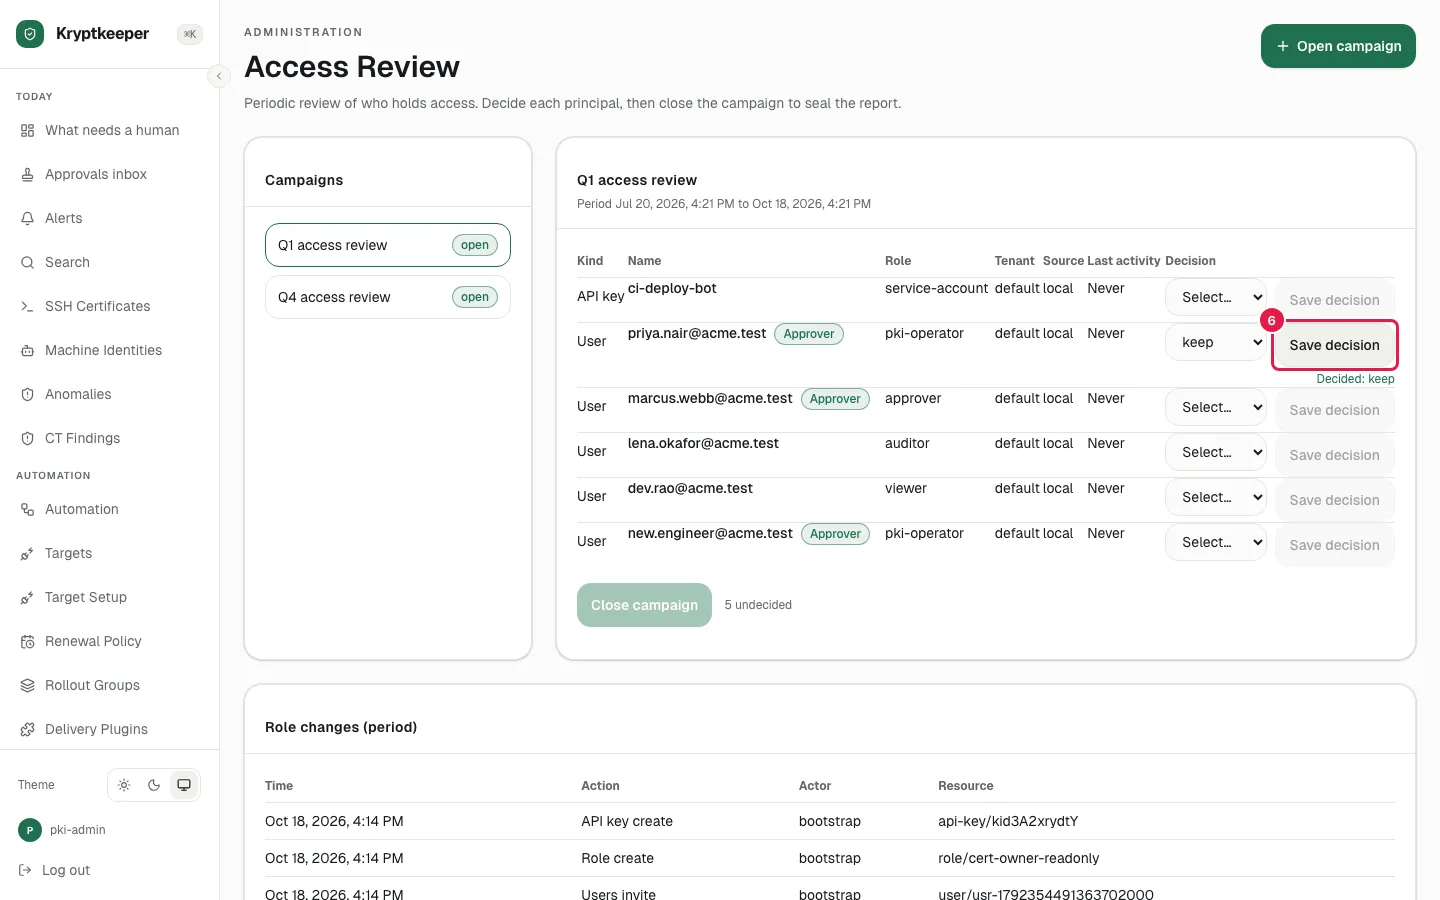
Access and tenancy Run an access review
Confirm or remove each person's access on a schedule.
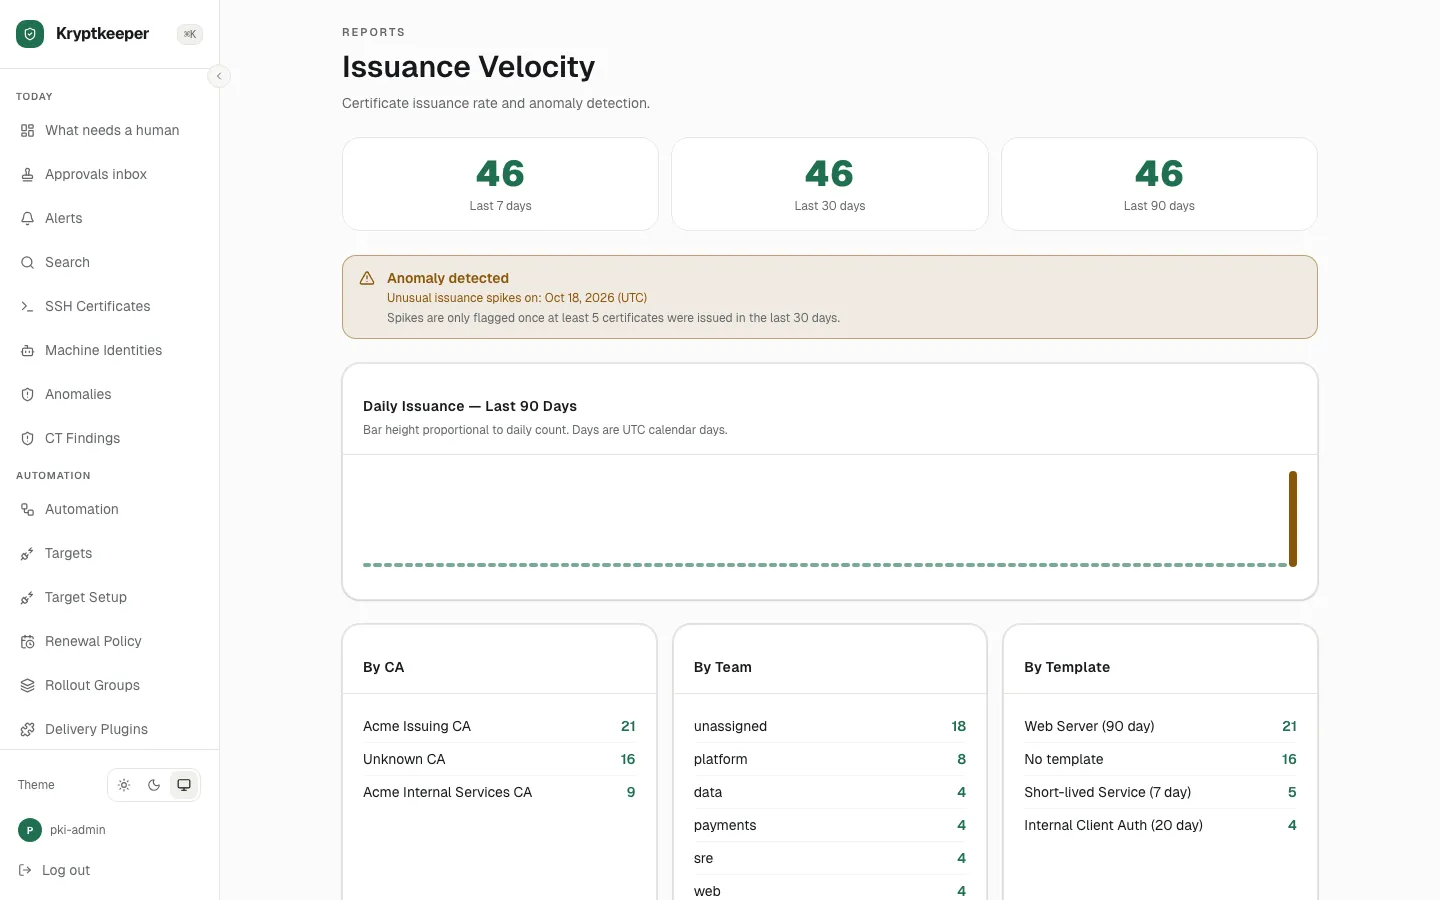
Compliance, risk and post-quantum Read the risk and post-quantum reports
See crypto posture, weak keys and post-quantum migration progress.
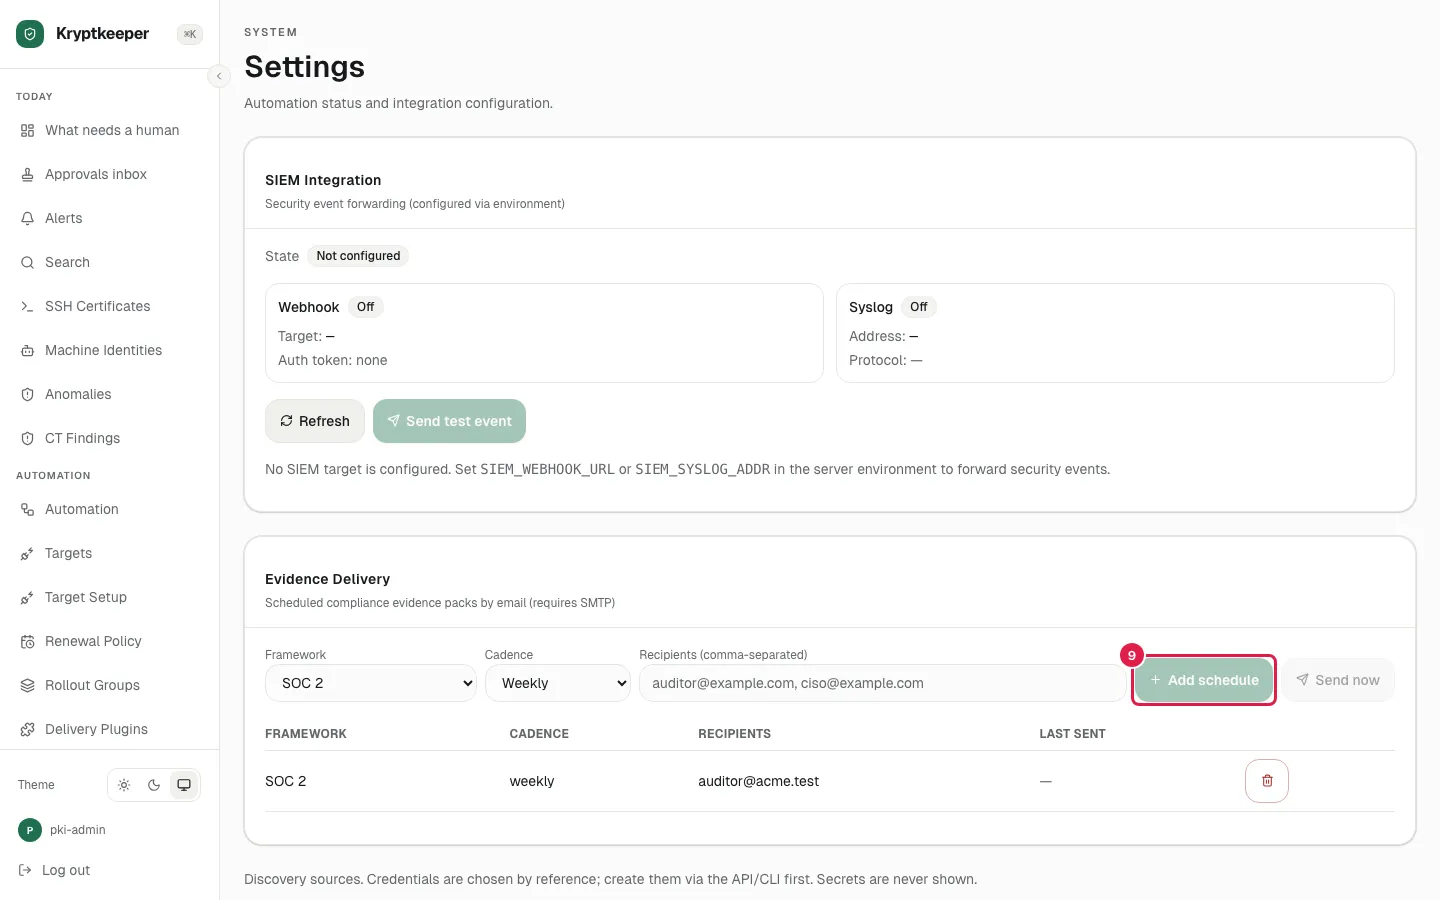
Compliance, risk and post-quantum Produce compliance evidence
Build an evidence pack or CBOM, or schedule it.
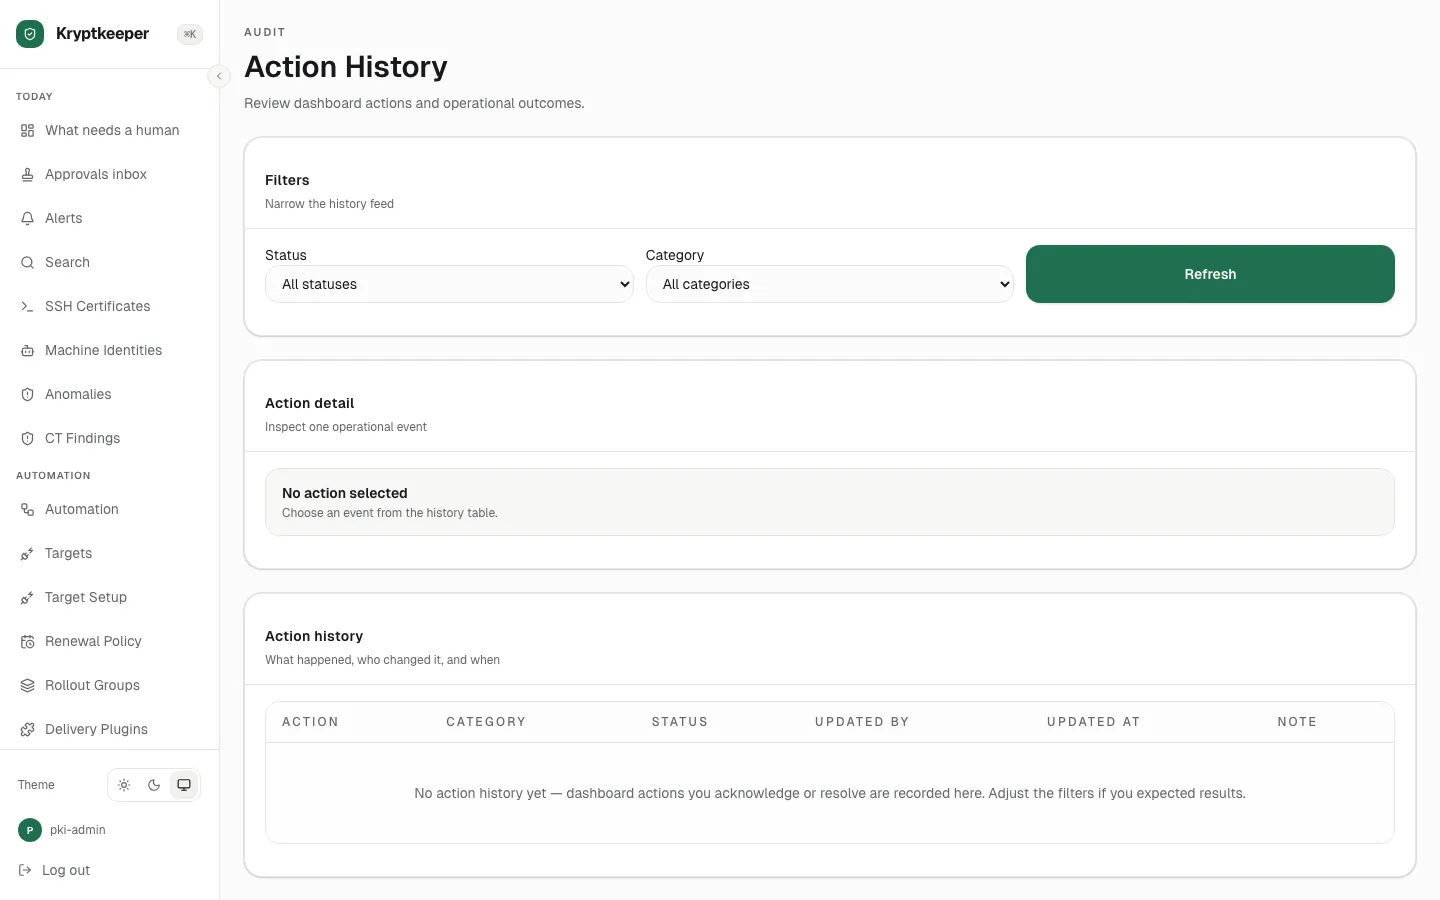
Compliance, risk and post-quantum Investigate with the audit trail
Follow who changed what, and when.