Linux and macOS hosts
Certificates that land on the host and renew themselves.
Run the lightweight agent on Linux and macOS, or manage hardened hosts agentlessly over SSH. Renewal policy is set per target, rollouts go canary first, and anything that fails lands in one queue.
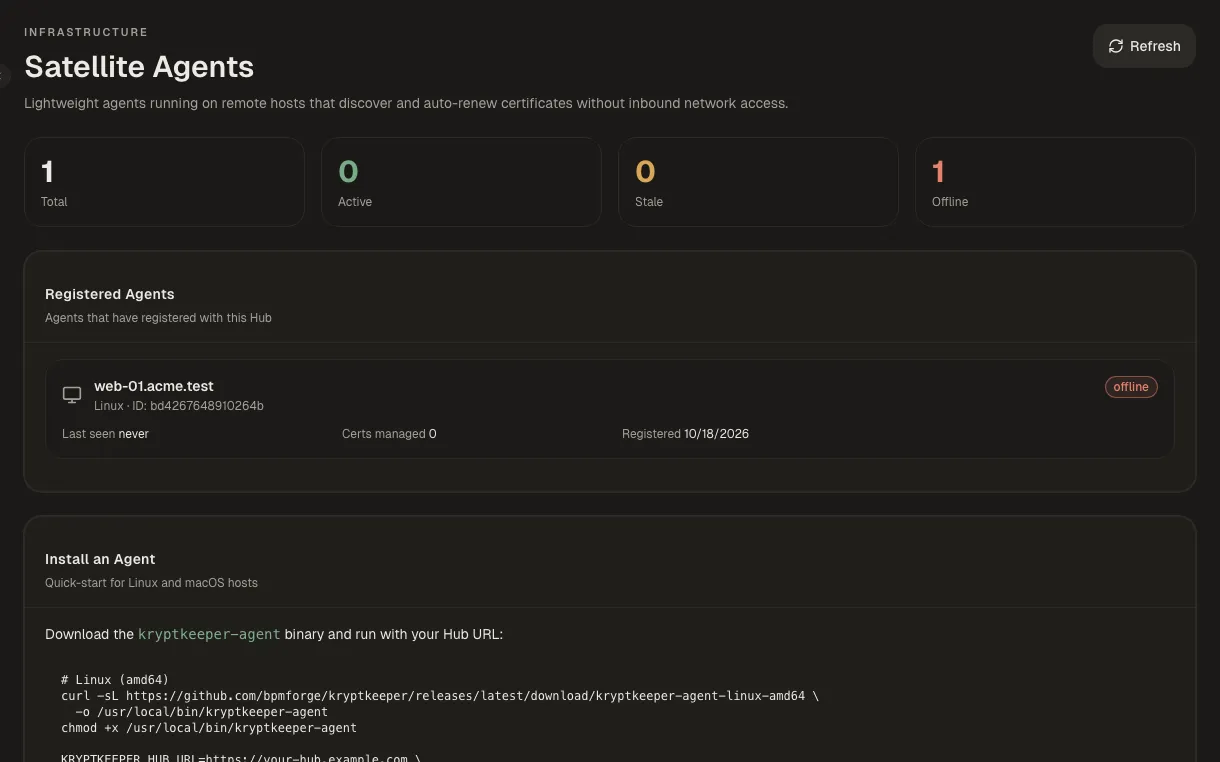
Coming: Screens from the host side (installing the agent, the certificate landing on disk and the service reloading) are being captured on the lab hosts and will be added here.
How it works
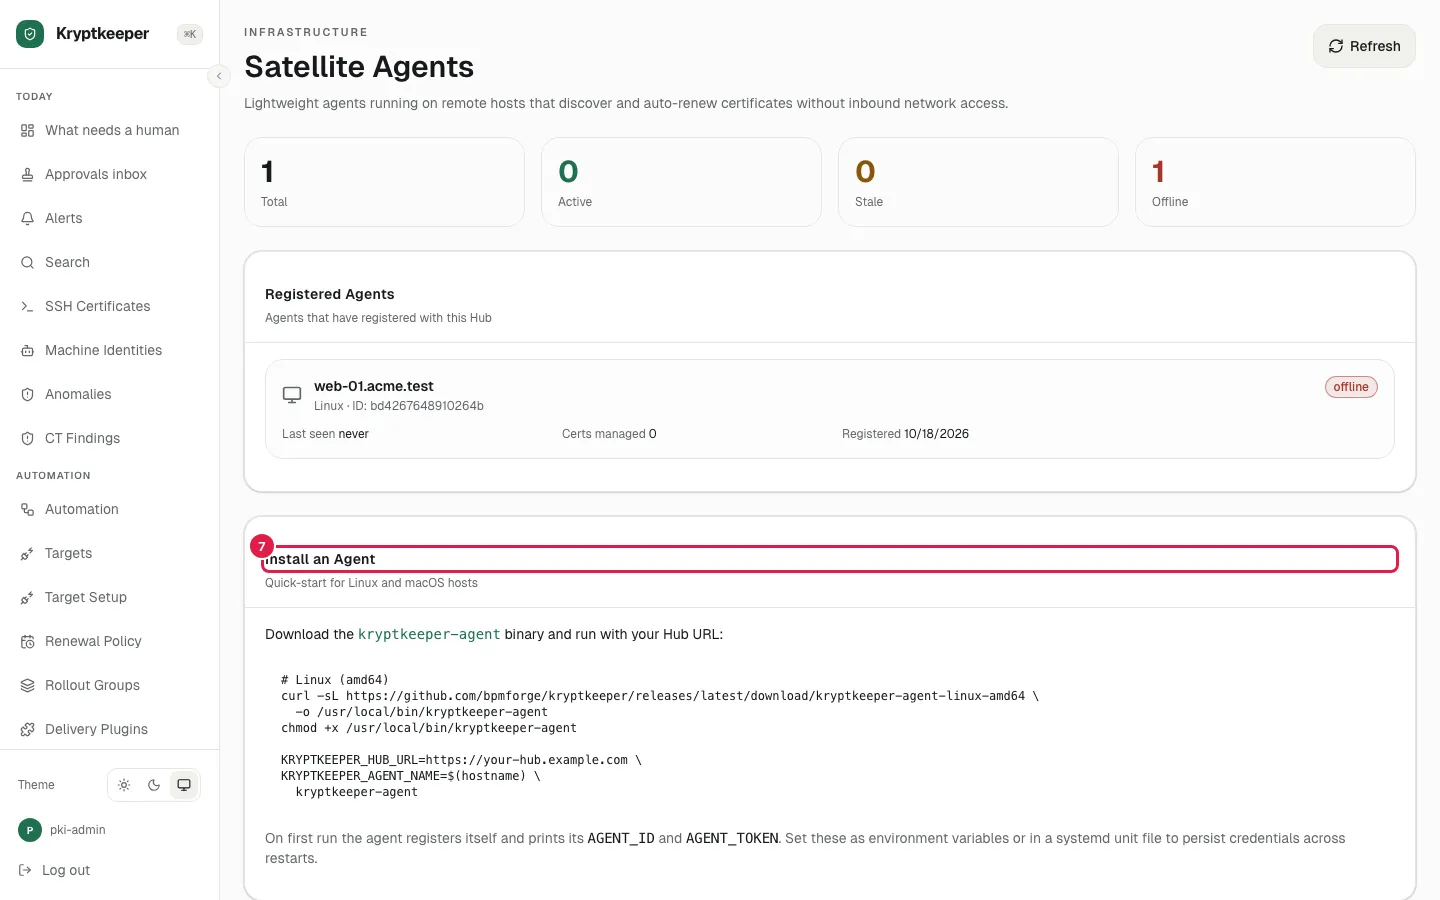
Enroll an agent
Enroll a Linux or macOS host so it can receive and renew certificates.
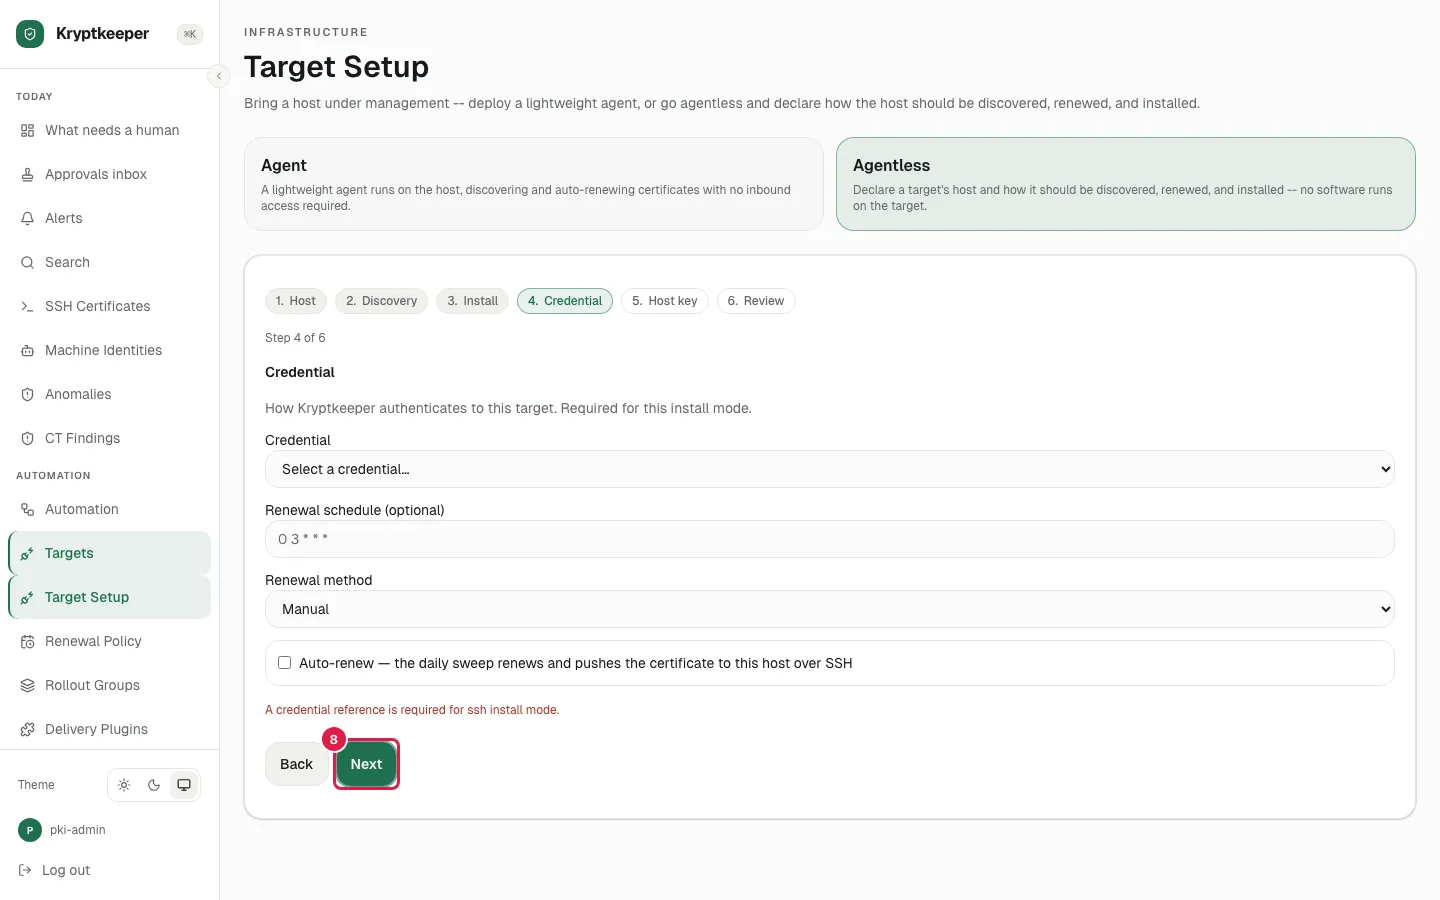
Manage a host without an agent
Bring a host under management over SSH, with no agent installed.
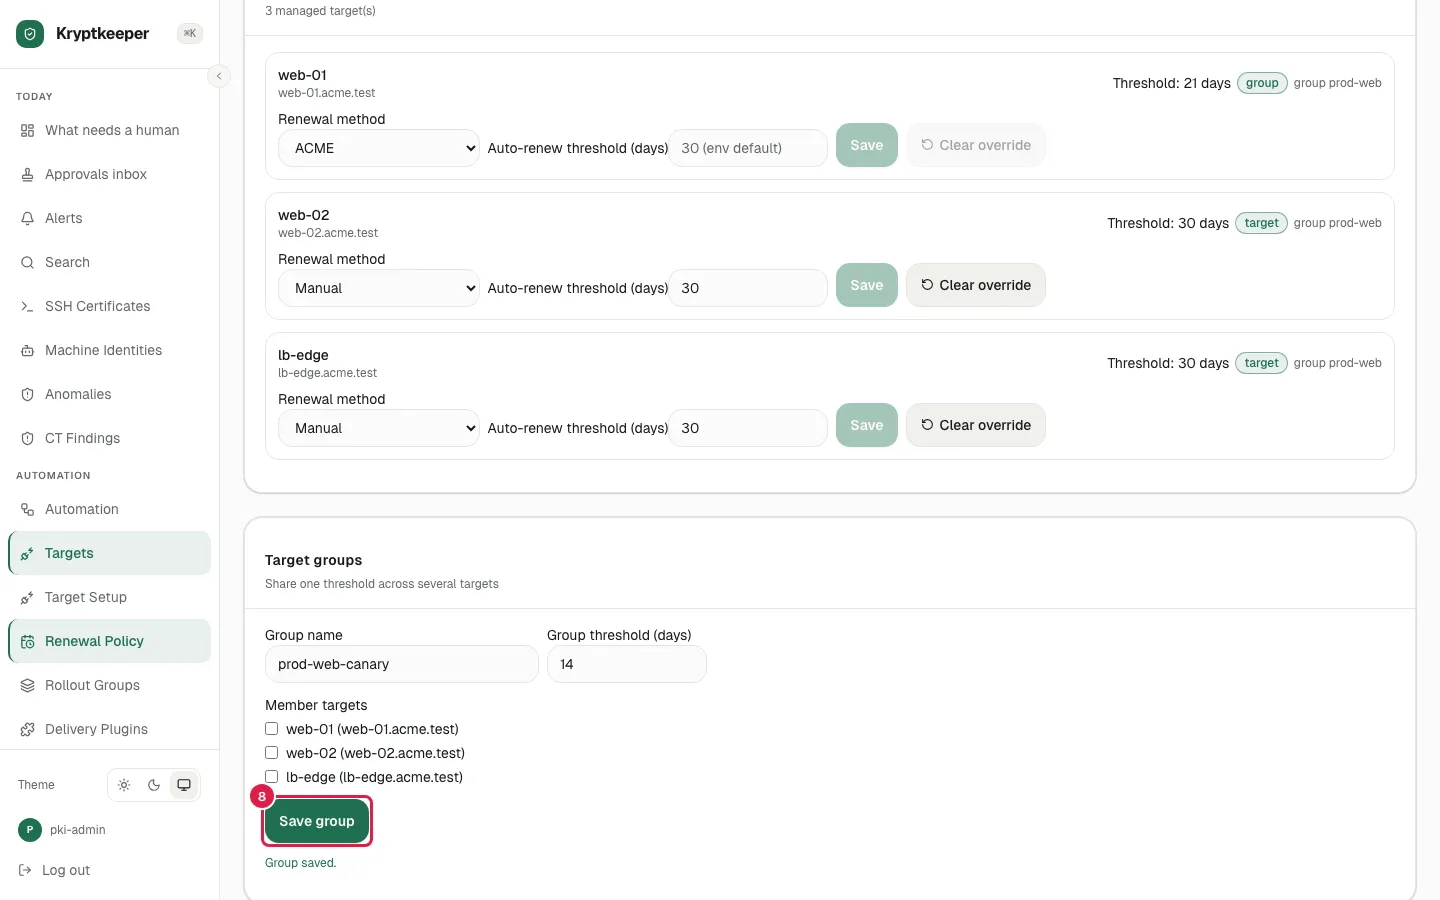
Set renewal policy per target
Decide when each target renews and how it is checked.
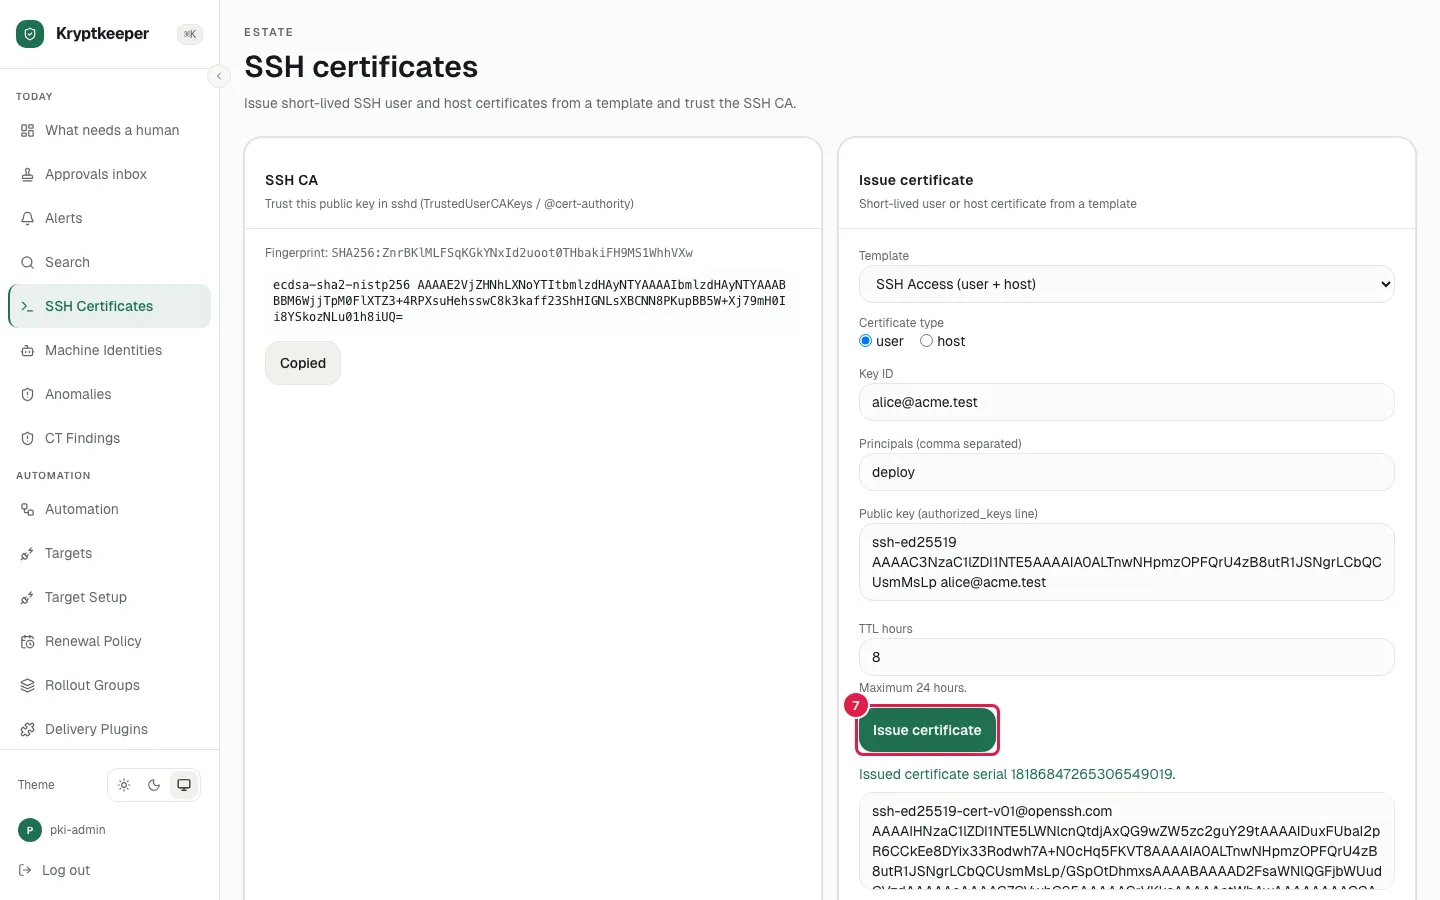
Issue SSH host and user certificates
Replace long-lived SSH keys with short-lived signed certificates.
Docs
Paths that use this
- Automate renewal for servers and devices for Platform and DevOps engineer