Approvals and guardrails
Sensitive changes need a second person, and show their impact first.
Requests, policies and exceptions can require a second approver. Before anything destructive, Kryptkeeper shows the blast radius: what will break and who owns it.
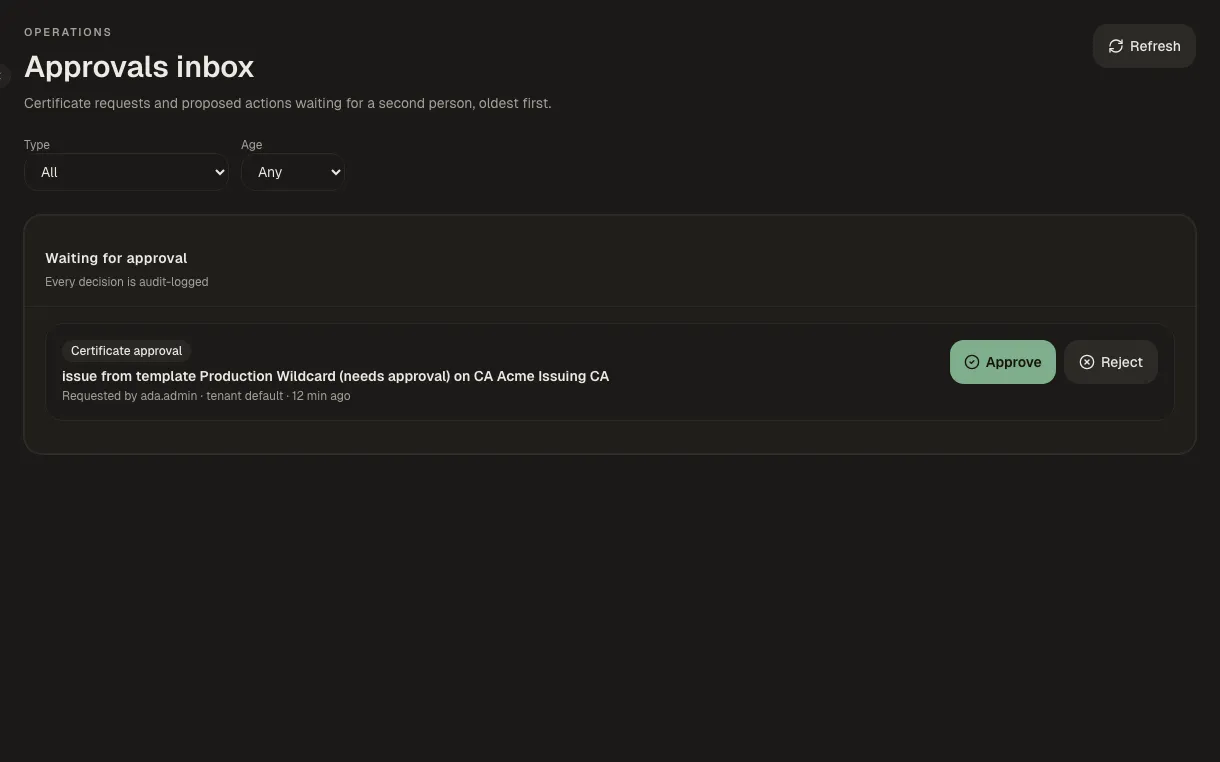
How it works
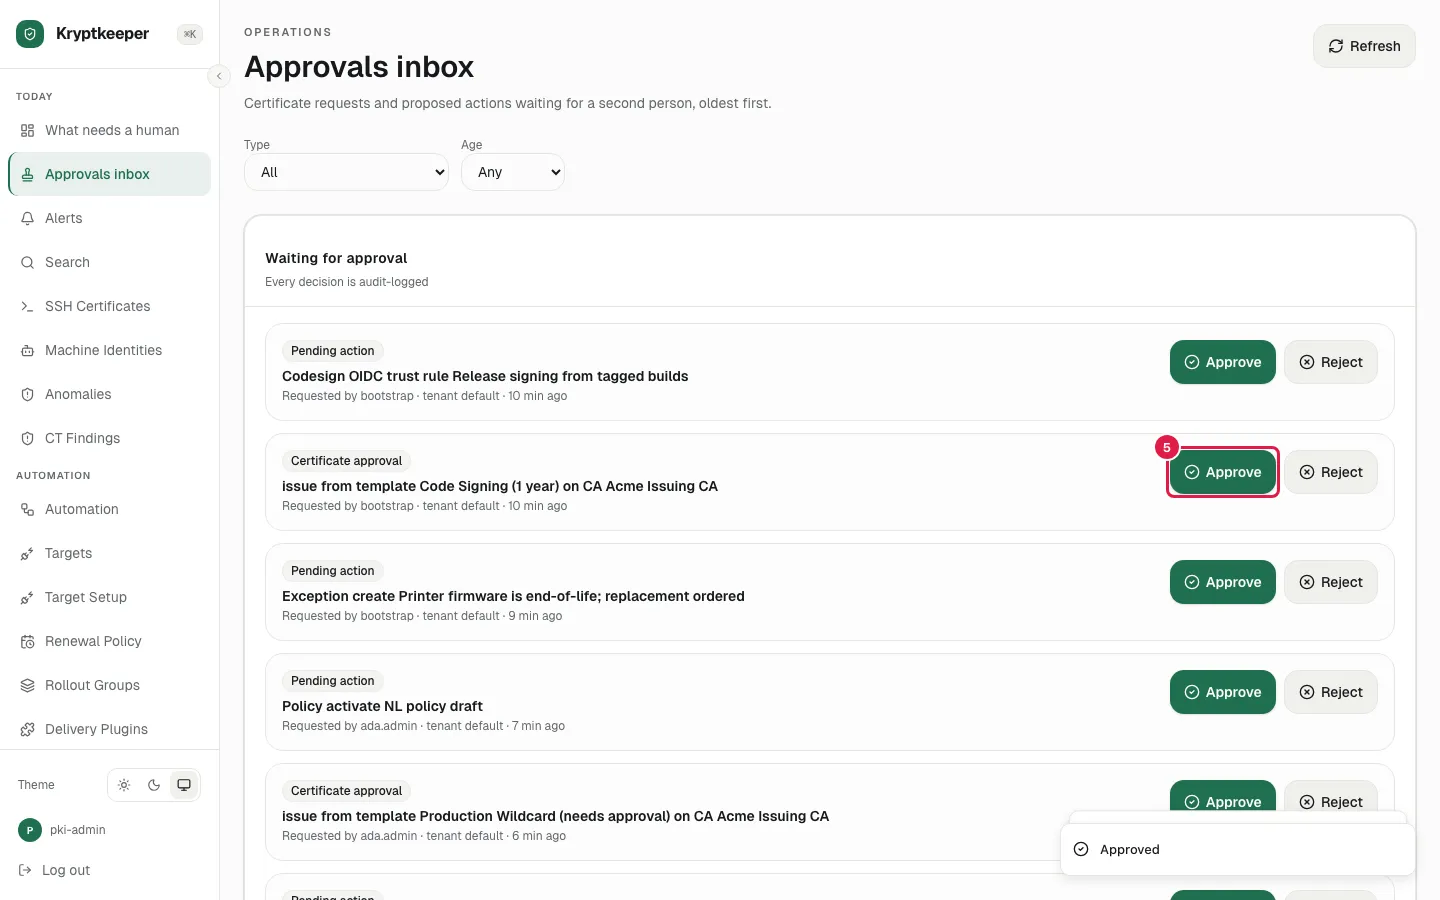
Approve a pending request
A second person reviews and approves a certificate request.
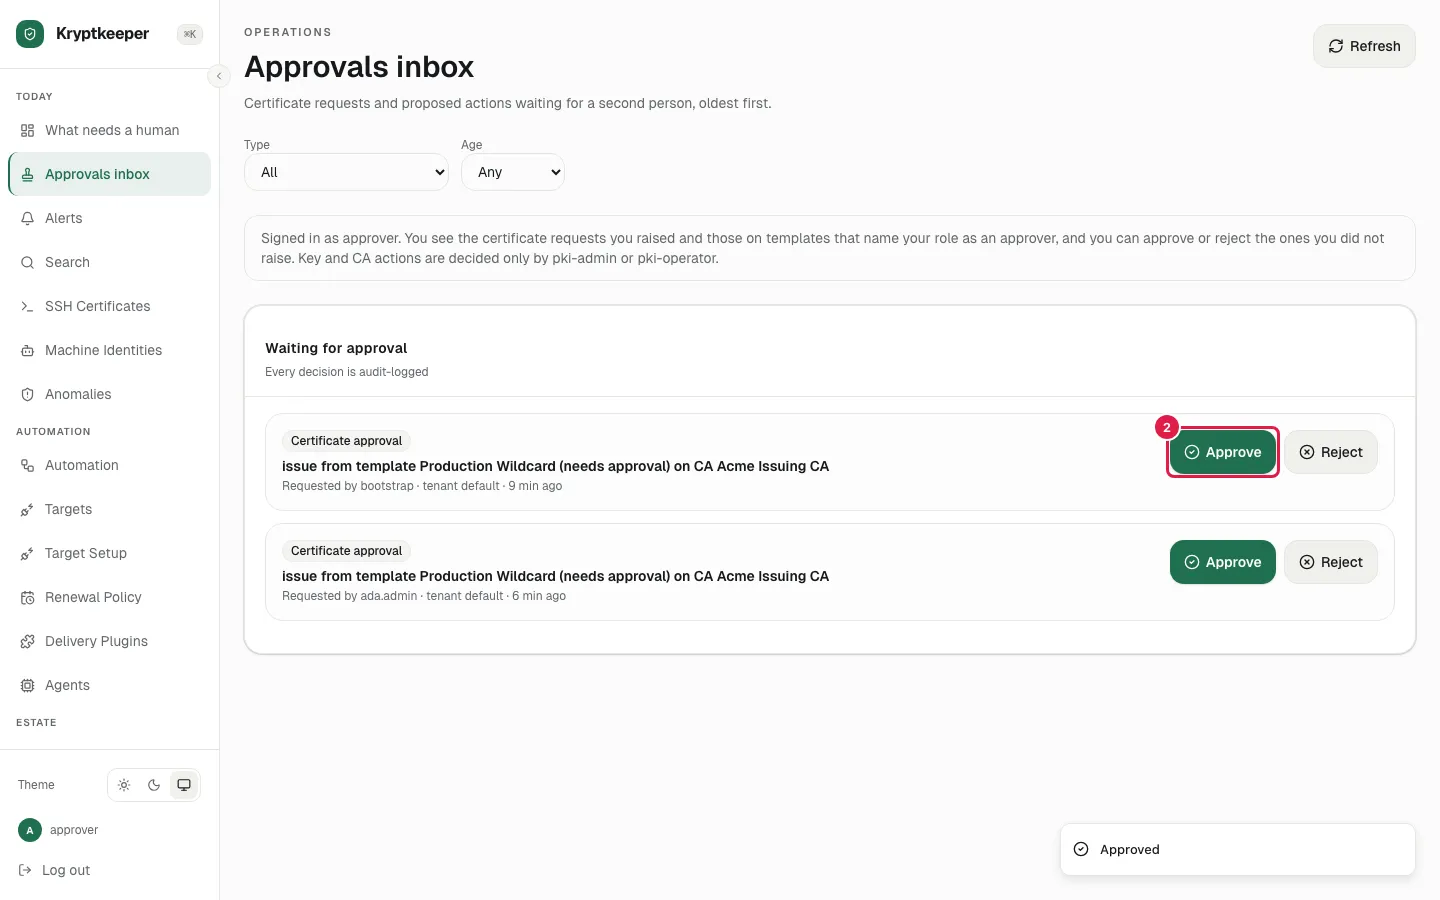
Decide requests with the approver role
A dedicated approver decides requests on the templates that name them.
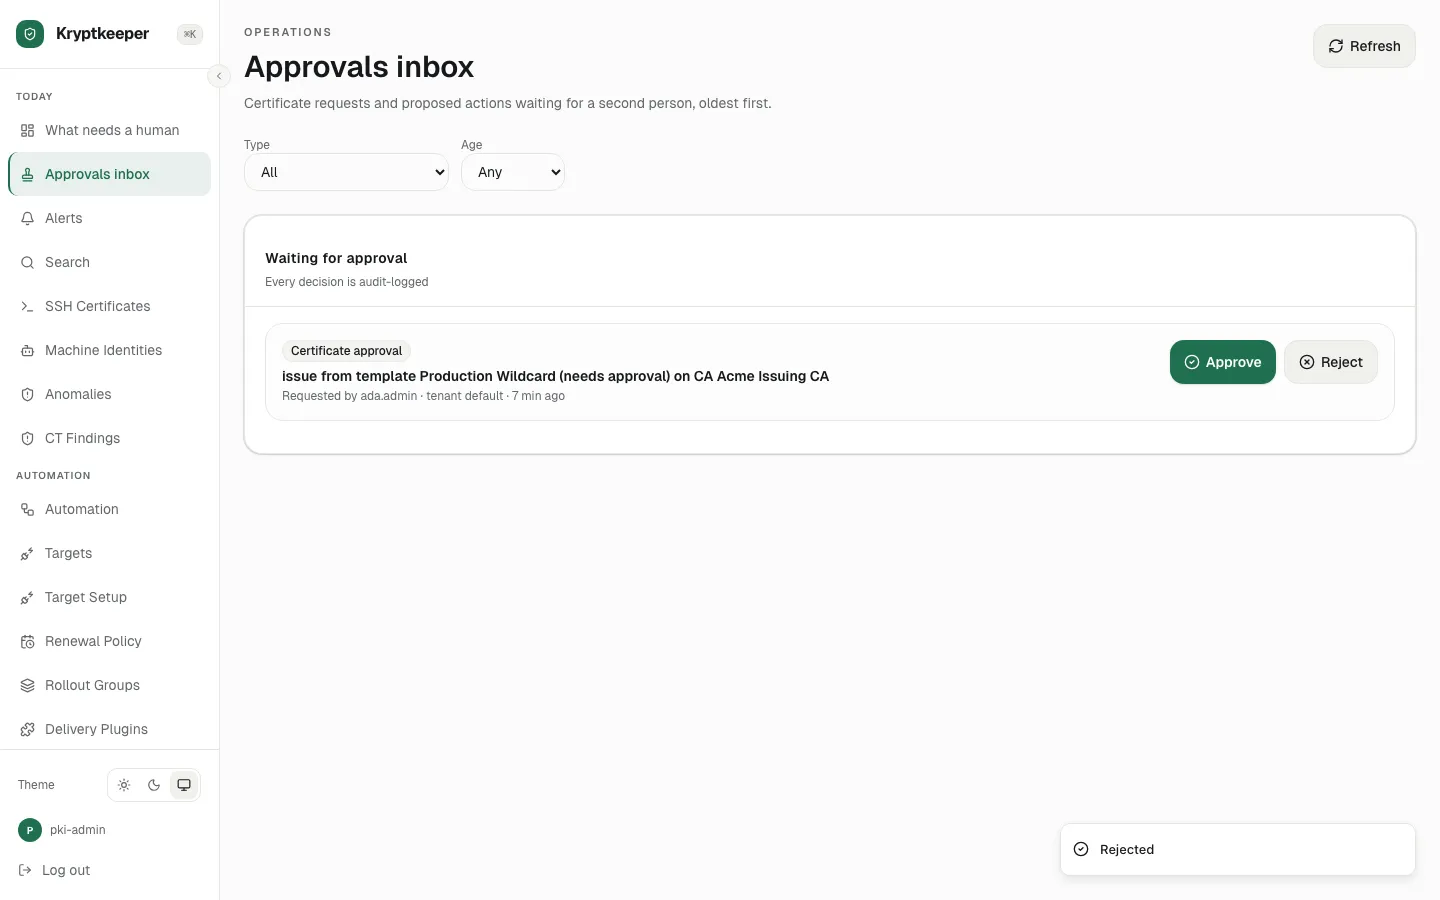
Reject a request
Turn a request down with a reason the requester can read.
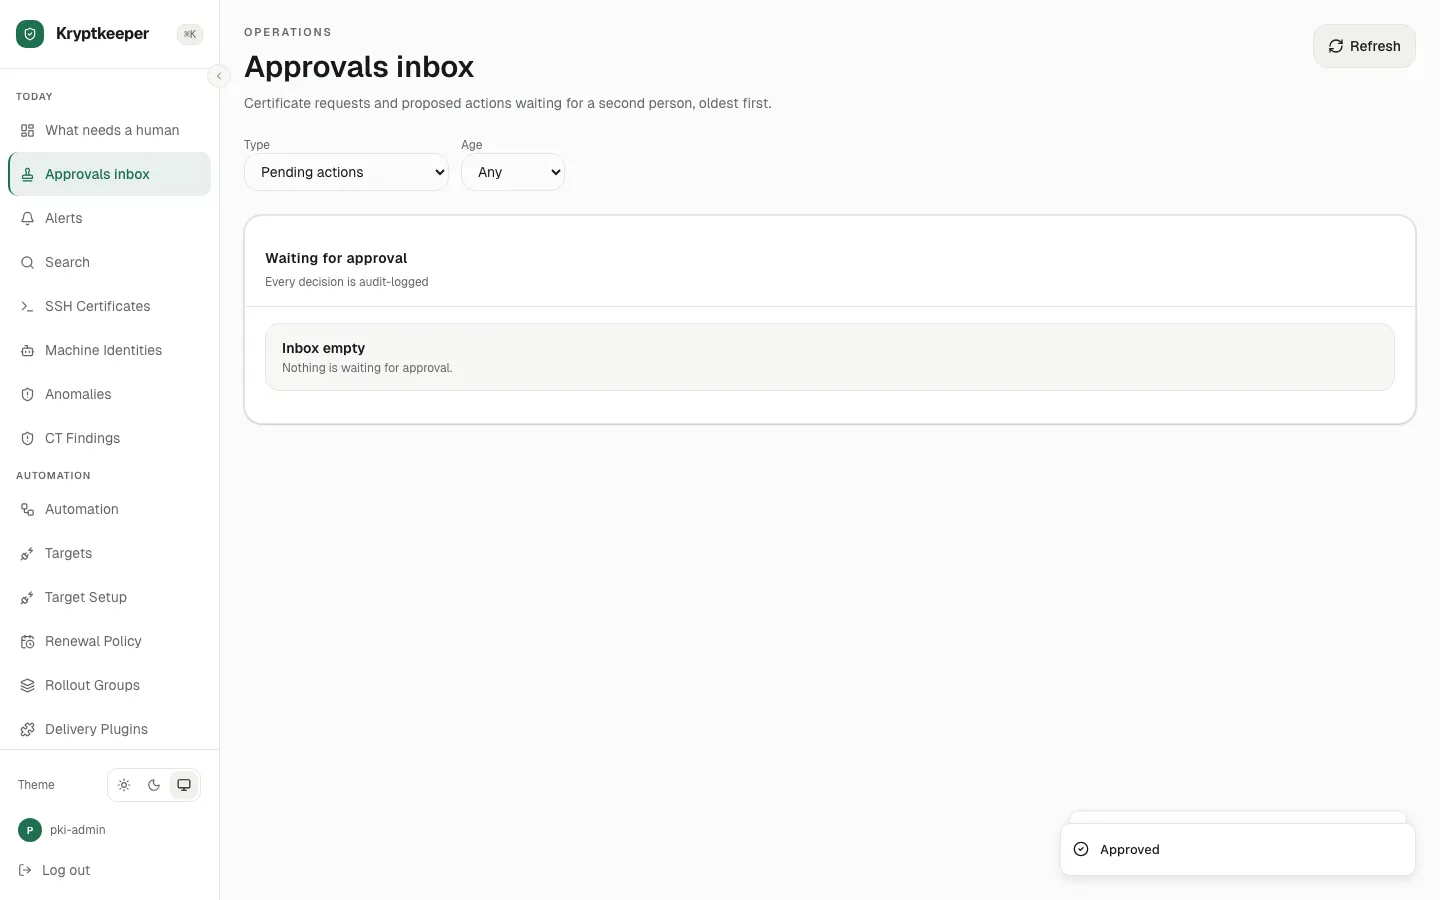
Approve a policy or exception
Approve a proposed policy change or risk exception before it takes effect.
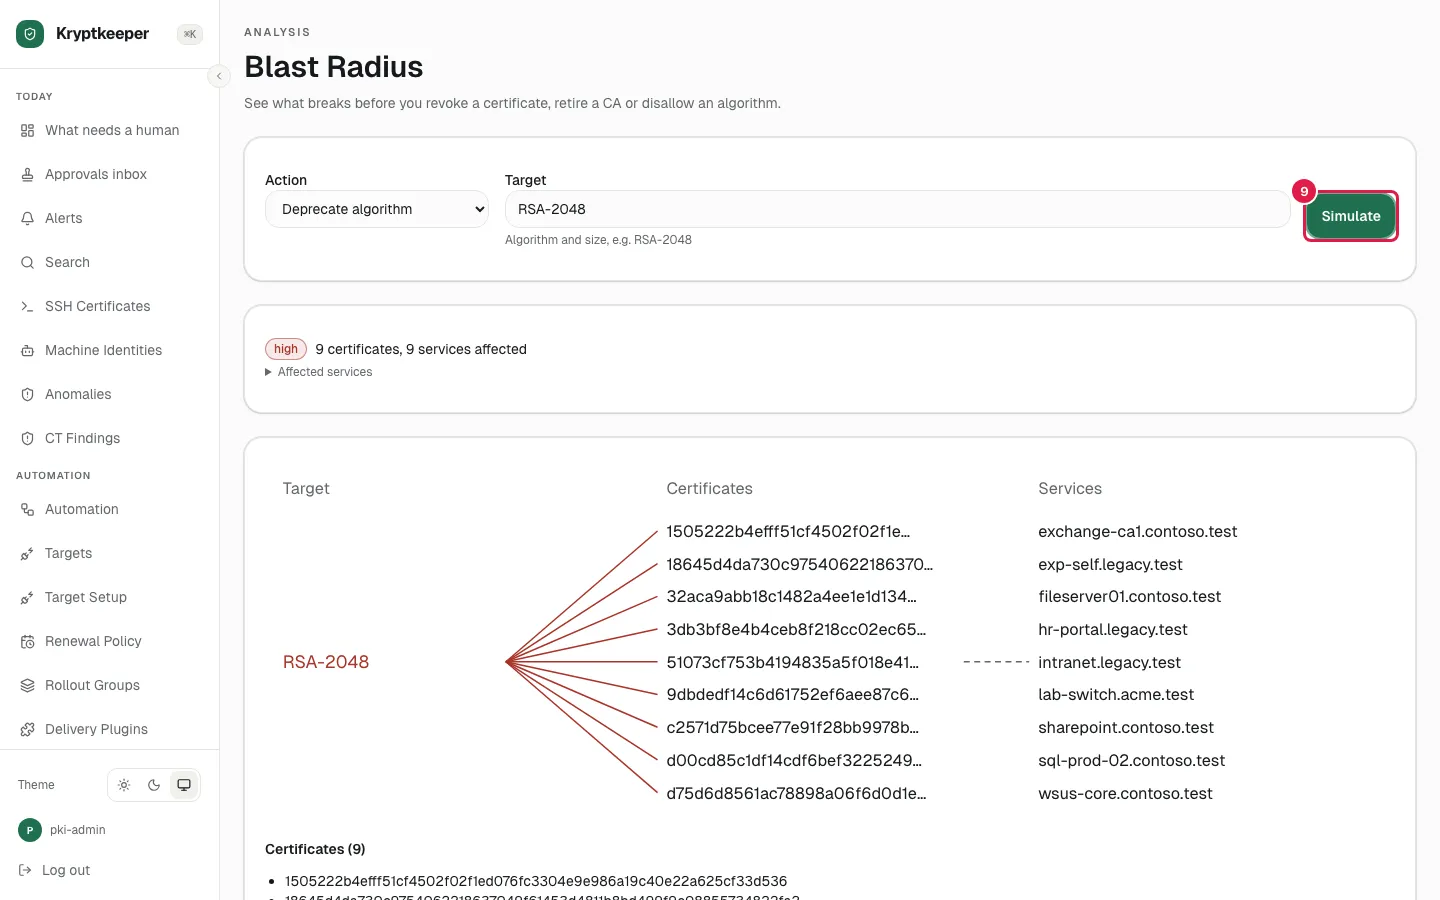
Check the blast radius first
See every certificate and service a destructive change would affect.
Paths that use this
- Govern it and prove it for Security and audit