Automation and enrollment
Speaks the protocols your clients already use.
Servers renew over ACME, devices enroll over SCEP, EST or CMP, and agents or agentless targets install certificates where they are used. Rollouts go to a canary first, and failures wait in one queue.
How it works
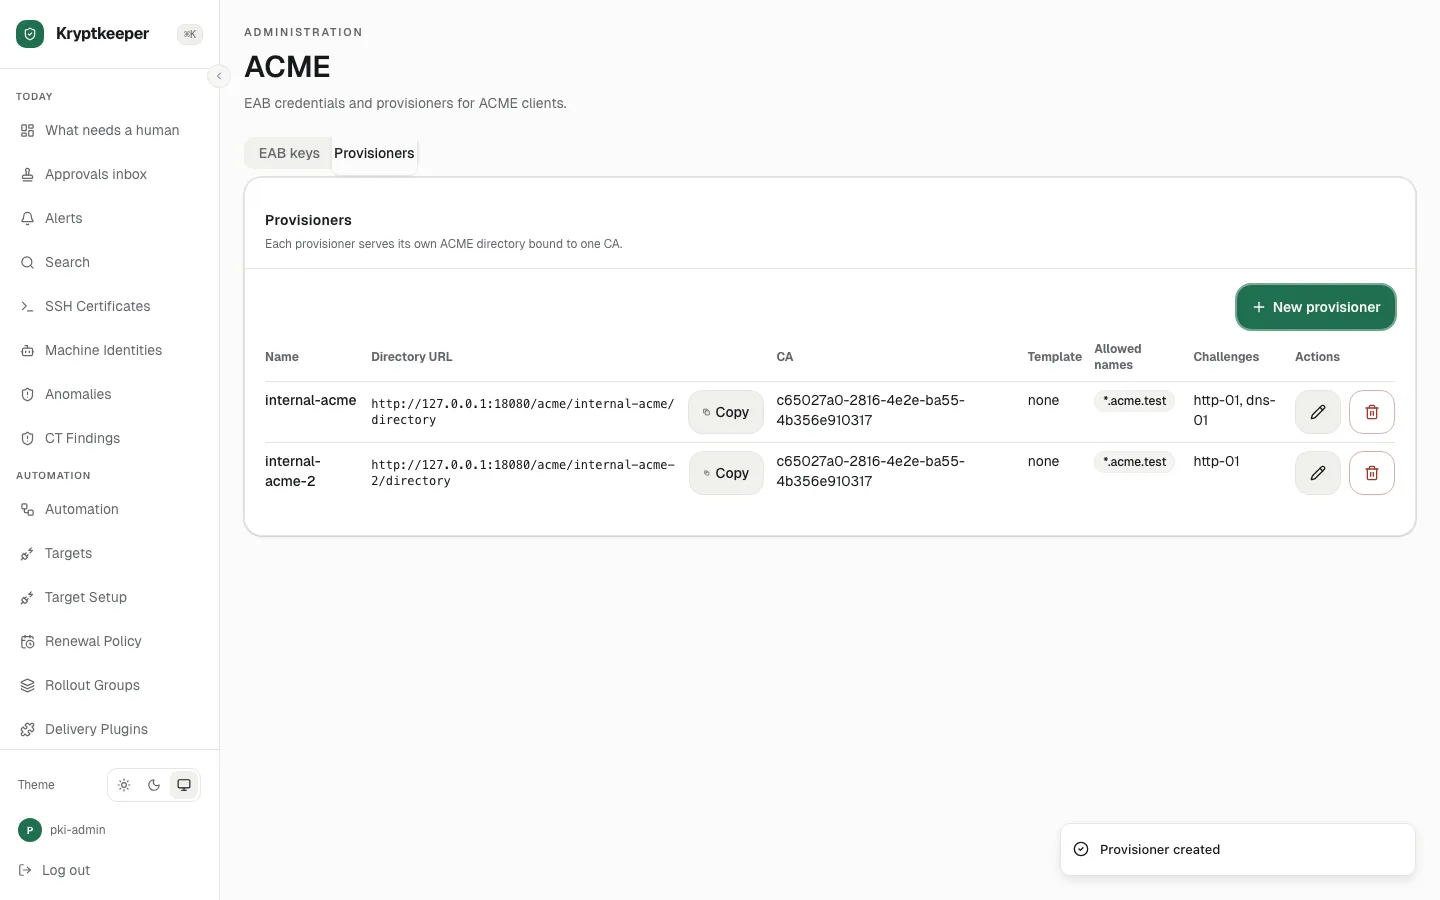
Set up ACME for a server
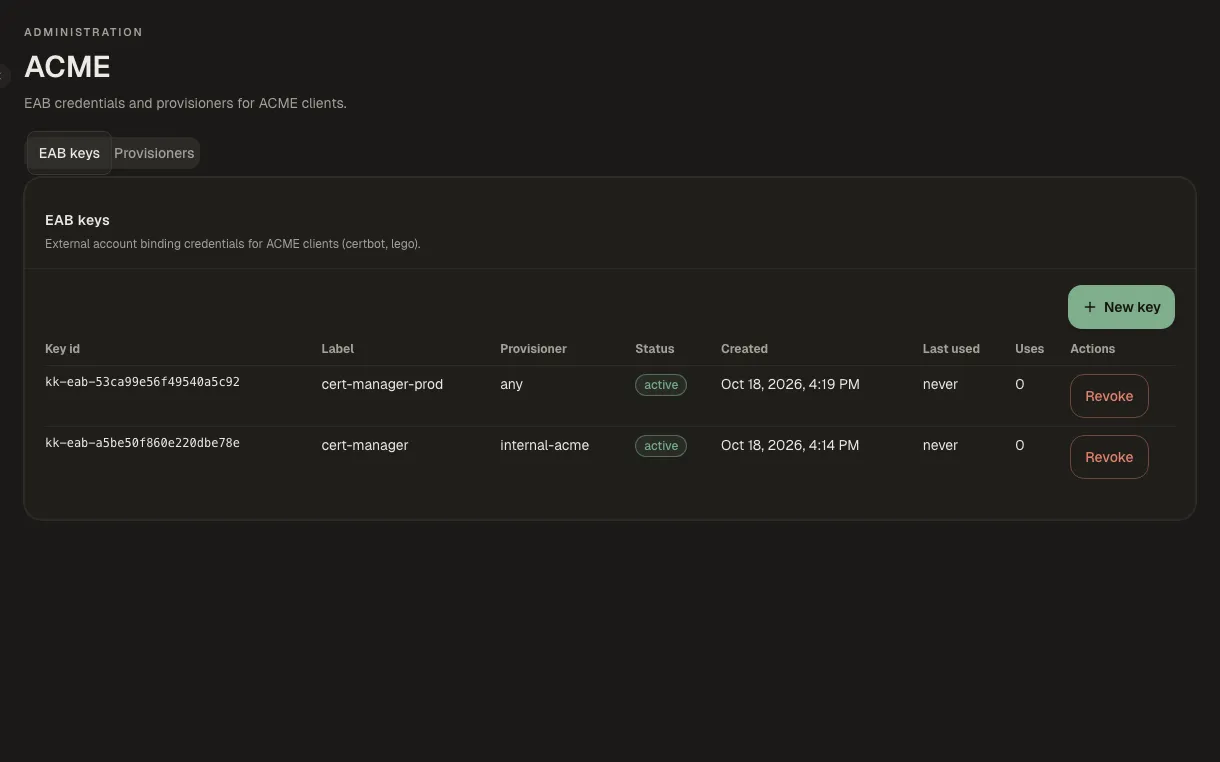
Create a provisioner and EAB key, then point an ACME client at it.
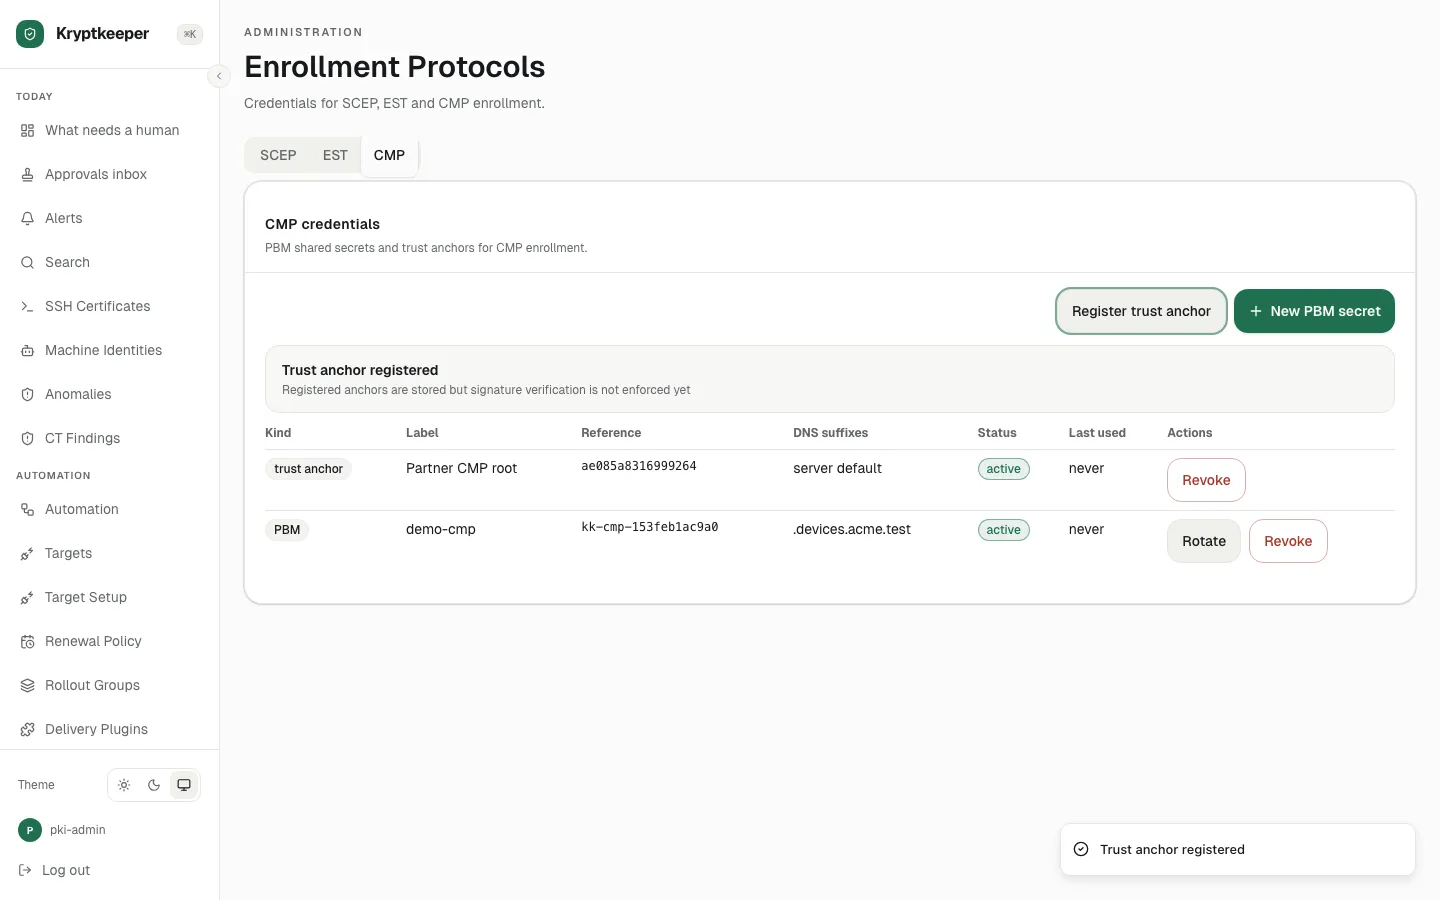
Enroll devices with SCEP, EST or CMP
Configure device enrollment and see a device enroll.
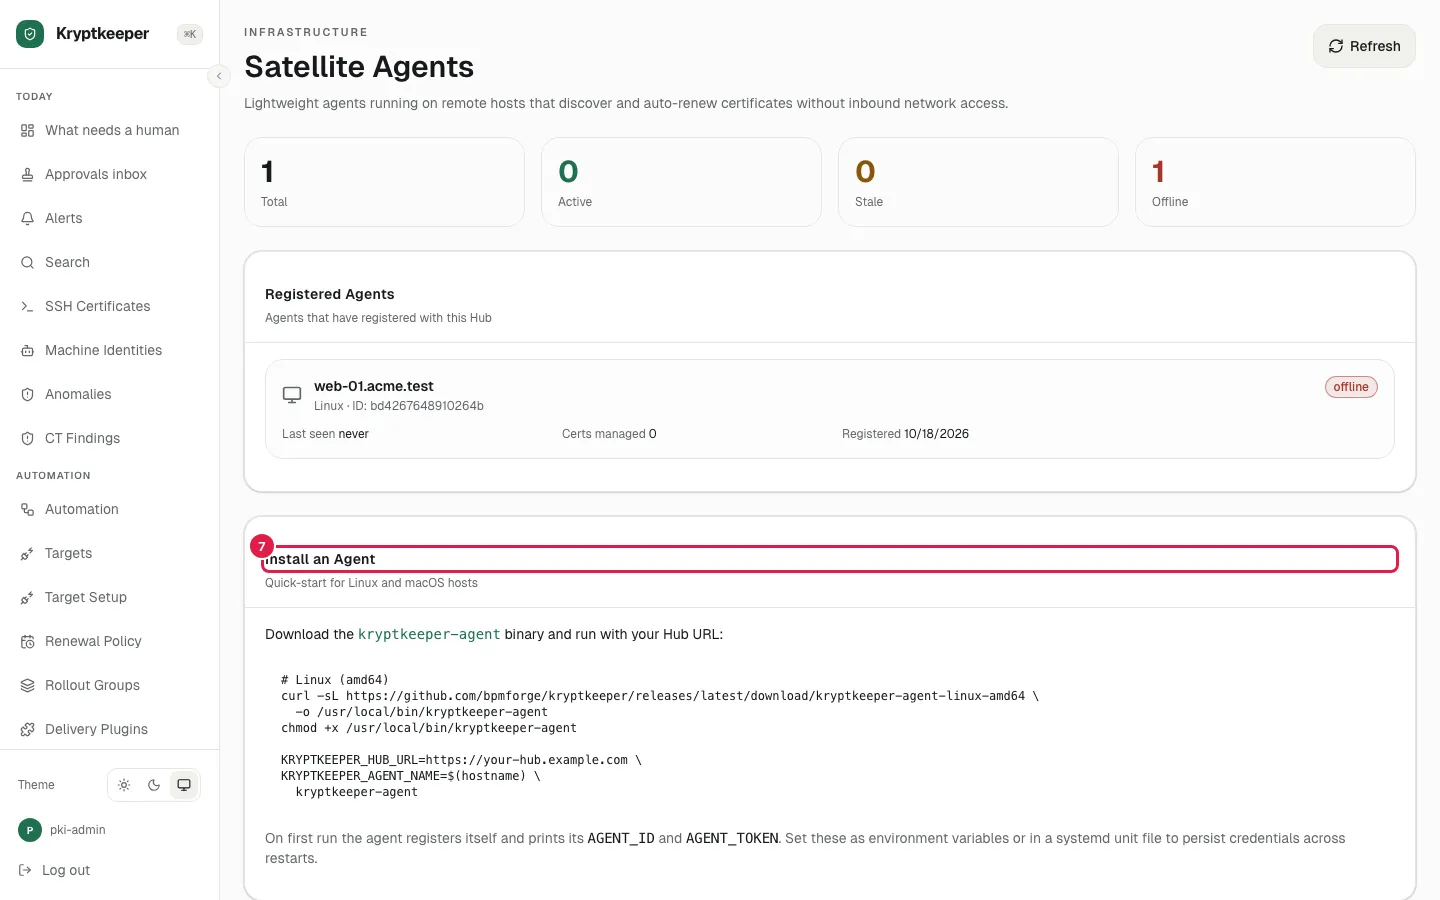
Enroll a satellite agent
Enroll an agent that installs certificates on its host.
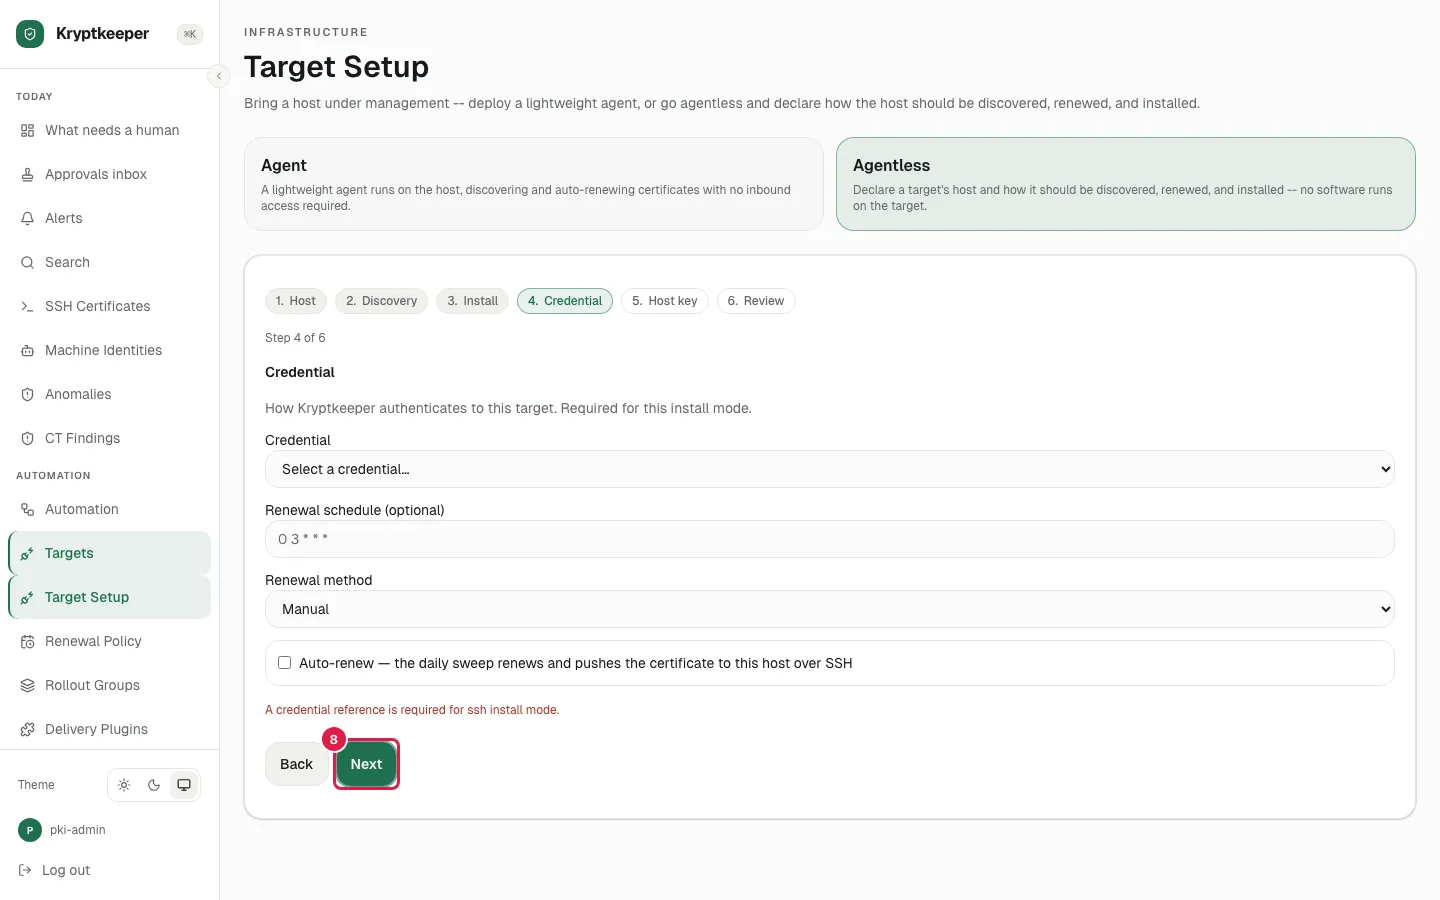
Add an agentless target
Manage a target over SSH or WinRM with nothing installed.
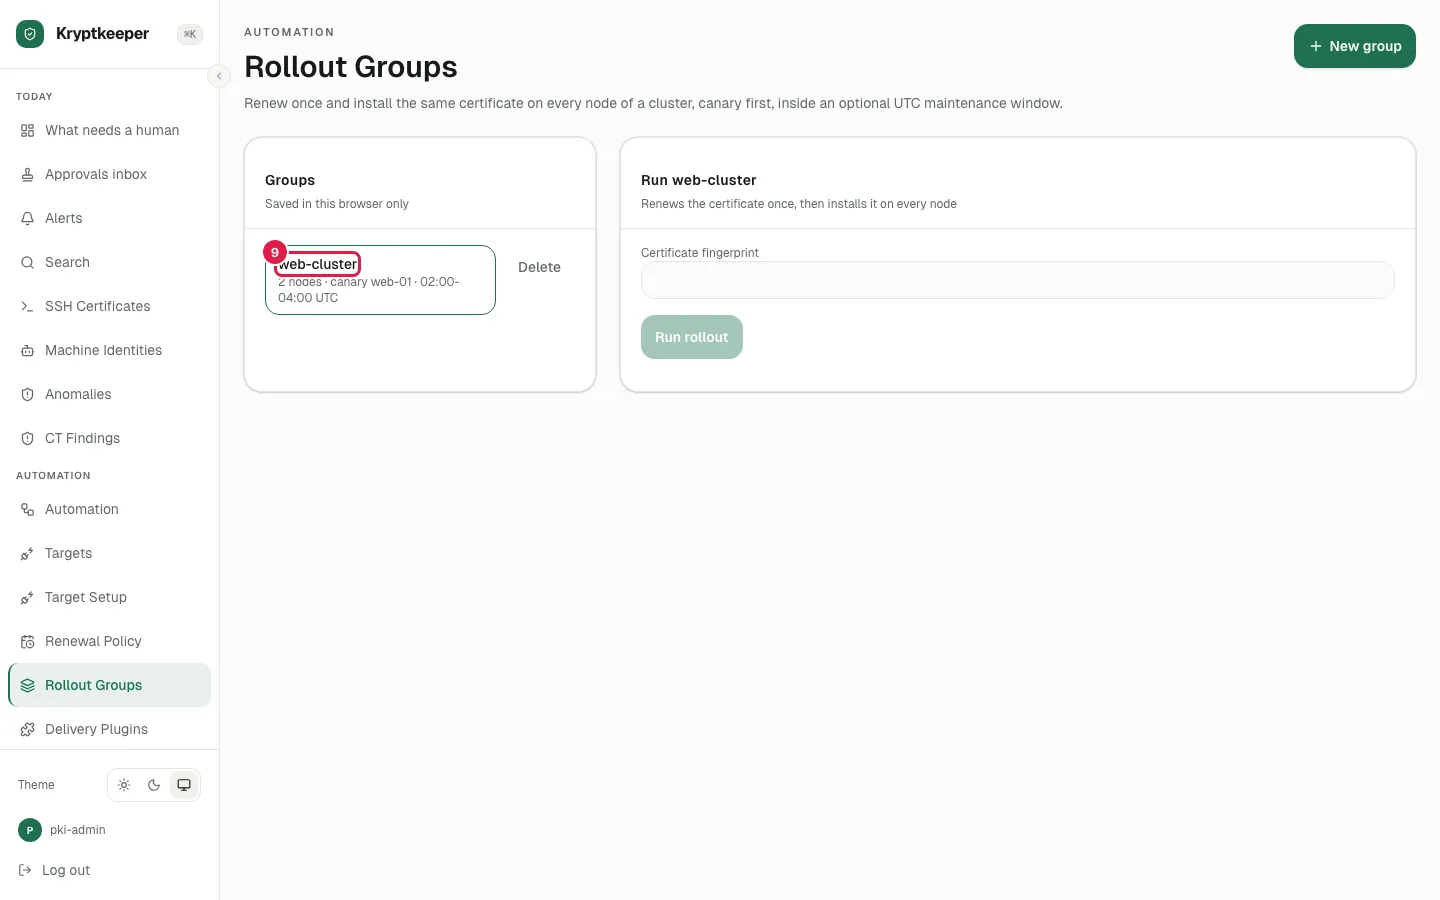
Roll out to a cluster, canary first
Send a certificate to one node, check it, then the rest.
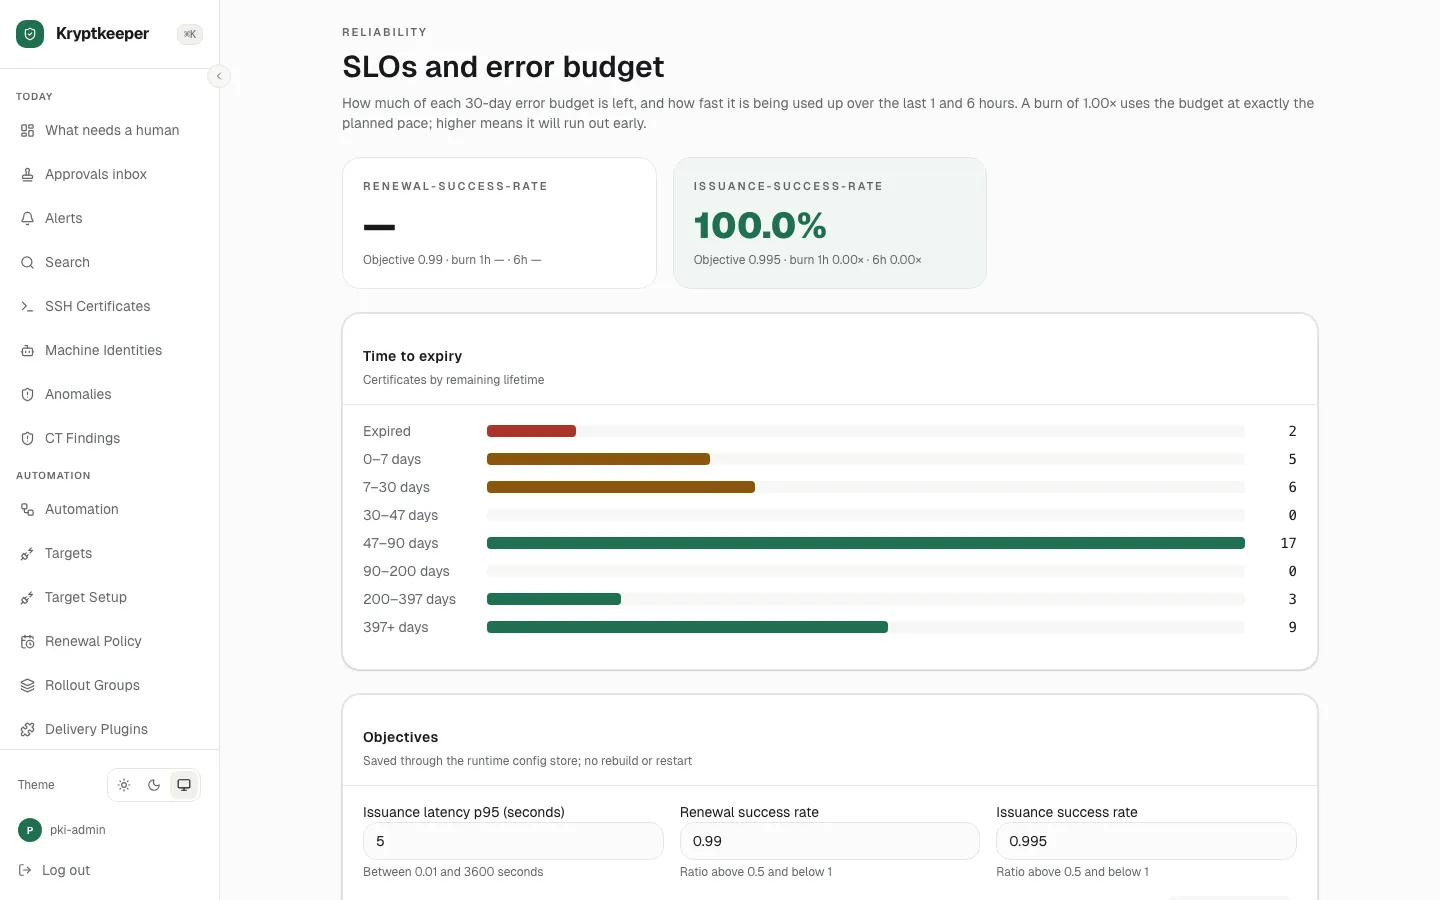
Watch the failed-renewal queue
See every renewal that needs a person, in one place.
Docs
Paths that use this
- Automate renewal for servers and devices for Platform and DevOps engineer